Securing Salesforce: Pentesting and Config Review.
Salesforce holds the personally identifiable information, and most of the real exposure sits in configuration rather than code. This guide covers both halves: how to pentest a Salesforce app, and how to review the settings that quietly expose records.
Cloud & SaaS
Salesforce
Pages:
59
Format:
PDF
Level:
Intermediate
Updated:
Oct 2026
Key Takeaways
- The components you are actually testing: Lightning components, Apex classes and controllers, Visualforce, Salesforce objects and fields, and SOQL.
- How to build your own Lightning app, public site and Lightning Web Component, so you can practise the techniques without touching a client org.
- The 3 access control layers and where each one fails: record level, field level and object level security.
- Config review using the tools Salesforce already gives you: Portal Health Checkup, Health Check, guest user sharing rule access, and Salesforce Optimizer.
What's inside
Salesforce is the most widely deployed CRM, which makes it a standing target for anyone after personally identifiable information, lifestyle data or behavioural data. The uncomfortable part is that a large share of real Salesforce exposure comes from sharing rules and guest user permissions, not from an exploitable bug in code.
This guide covers both halves. The first is a working introduction to how a Salesforce app is built and how to pentest it, including access control testing and SOQL. The second is the configuration review: what to check, in what order, and which built-in tools surface it.
What the 59 pages cover
01
Key components of a Salesforce app
p. 6
Lightning components, Apex, Visualforce, objects and fields, and SOQL.
02
Creating your own Salesforce app instance
p. 10
A Lightning application, a public site and a Lightning Web Component, built from scratch.
03
Access control policies: RLS, FLS and OLS
p. 22
Record, field and object level security, and how each is bypassed in practice.
04
Salesforce app pentesting
p. 25
Methodology, tooling, and the vulnerability classes that recur across orgs.
05
Configuration review
p. 47
What to inspect in the org itself, and the order that finds the most in the least time.
06
Useful tools for config review
p. 51
Portal Health Checkup, Health Check, guest user sharing rules, and Salesforce Optimizer.
Look inside
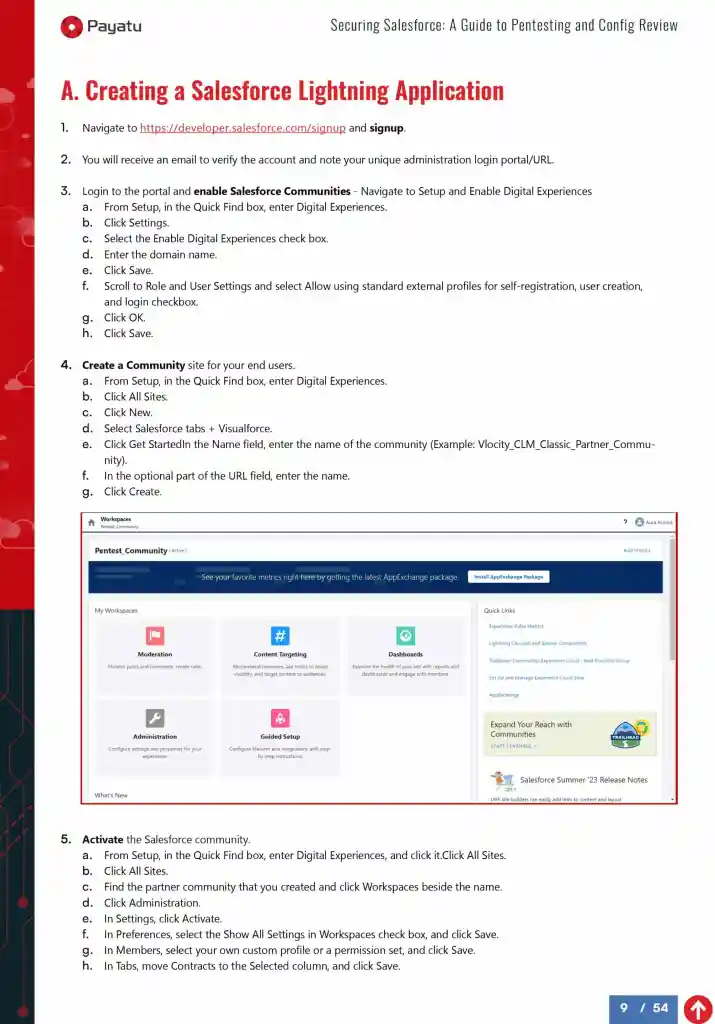
A sample spread — the level of detail in every chapter.
Written by Payatu's cloud and application security team
Run it against your own org
The full 59-page PDF, with the pentesting methodology, the access control tests, and the configuration review checklist in one working reference.