
Learn the API Top 10 by breaking it
DVAPI turns the OWASP API Security Top 10 for 2023 into ten hands-on challenges. Clone it, run it locally, and work through every risk from BOLA to unsafe consumption of APIs.


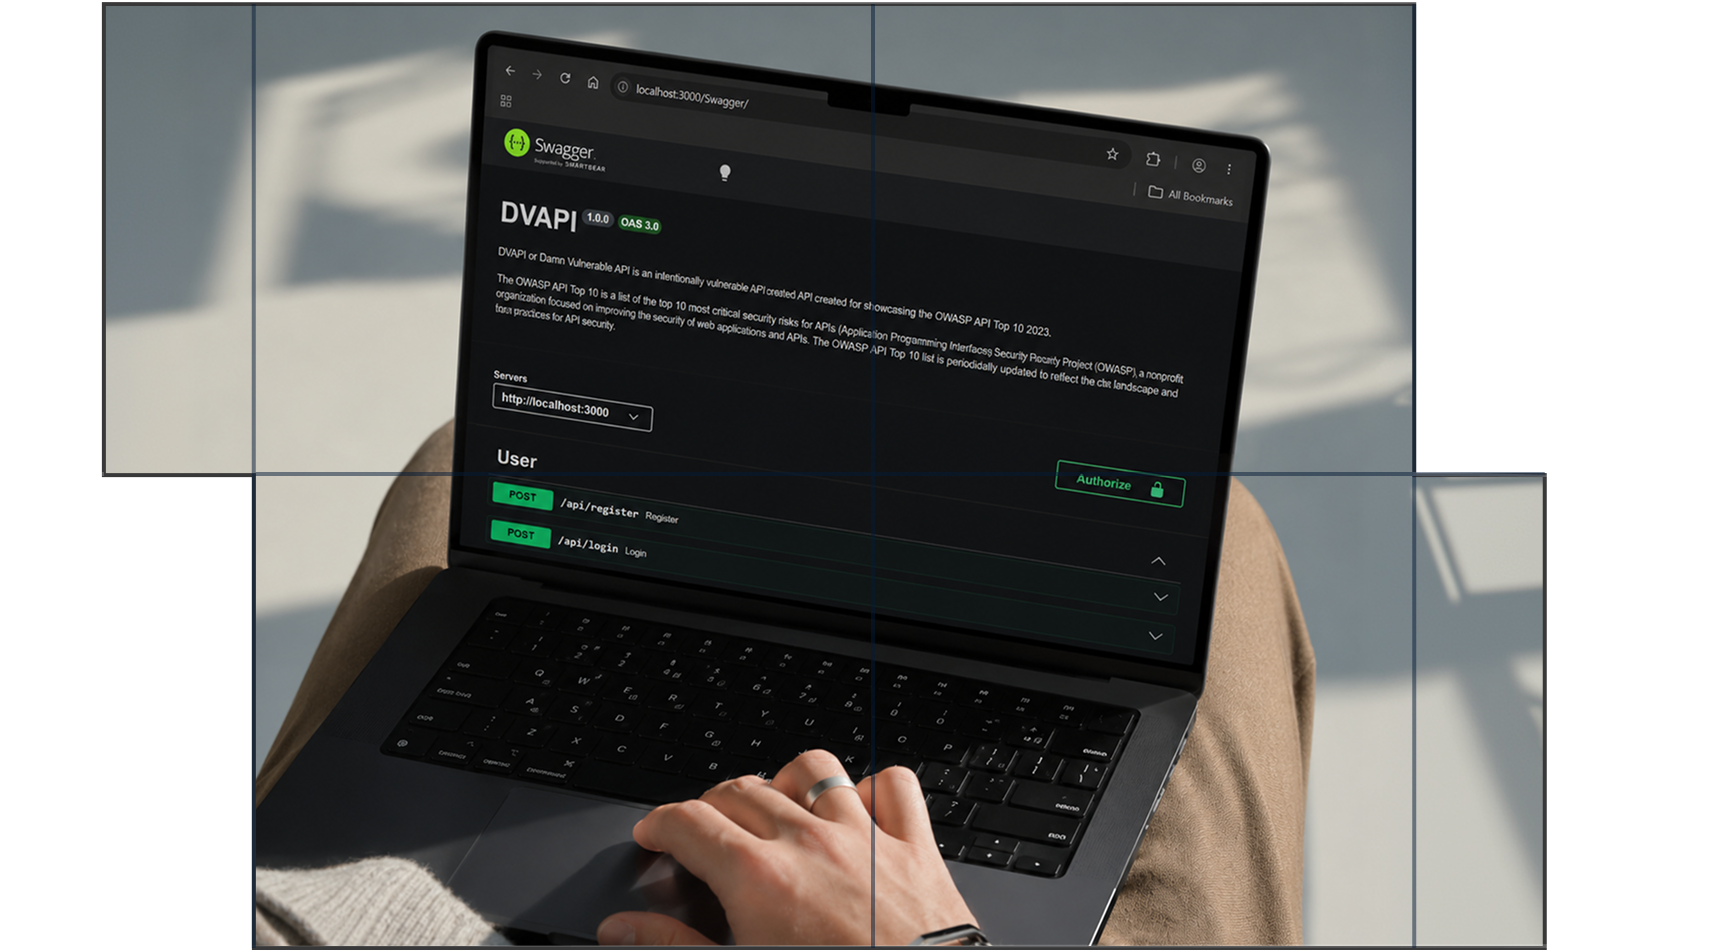
Meet dvapi
The vulnerability catalog
Every flaw in DVAPI is one of the OWASP API Security Top 10. Learn it here, and you will recognise it in the wild.
Safe to attack
DVAPI runs on your own machine at 127.0.0.1, so nothing real is harmed and nothing is off-limits.
The real Top 10, not toy puzzles
Every challenge maps to a risk in the OWASP API Security Top 10 for 2023.
Flags mark your progress
Each challenge you crack yields a flag you submit in the app, so you can see how many of the ten you have cleared.
YOUR FIRST FLAG
How one challenge works, start to flag.
Challenge one is Broken Object Level Authorization, OWASP's number one API risk. Here is how you capture its flag.
01
You get an endpoint
The app gives you an API that returns your own records. The question it poses: can you read someone else's?
02
You change the ID
You request your own object, then swap the identifier for one that is not yours.
03
It just works
The API never checks whether the object belongs to you. That missing check is the bug: Broken Object Level Authorization.
04
You capture the flag
A successful exploit returns a flag string. Submit it in the app, and challenge one is done.
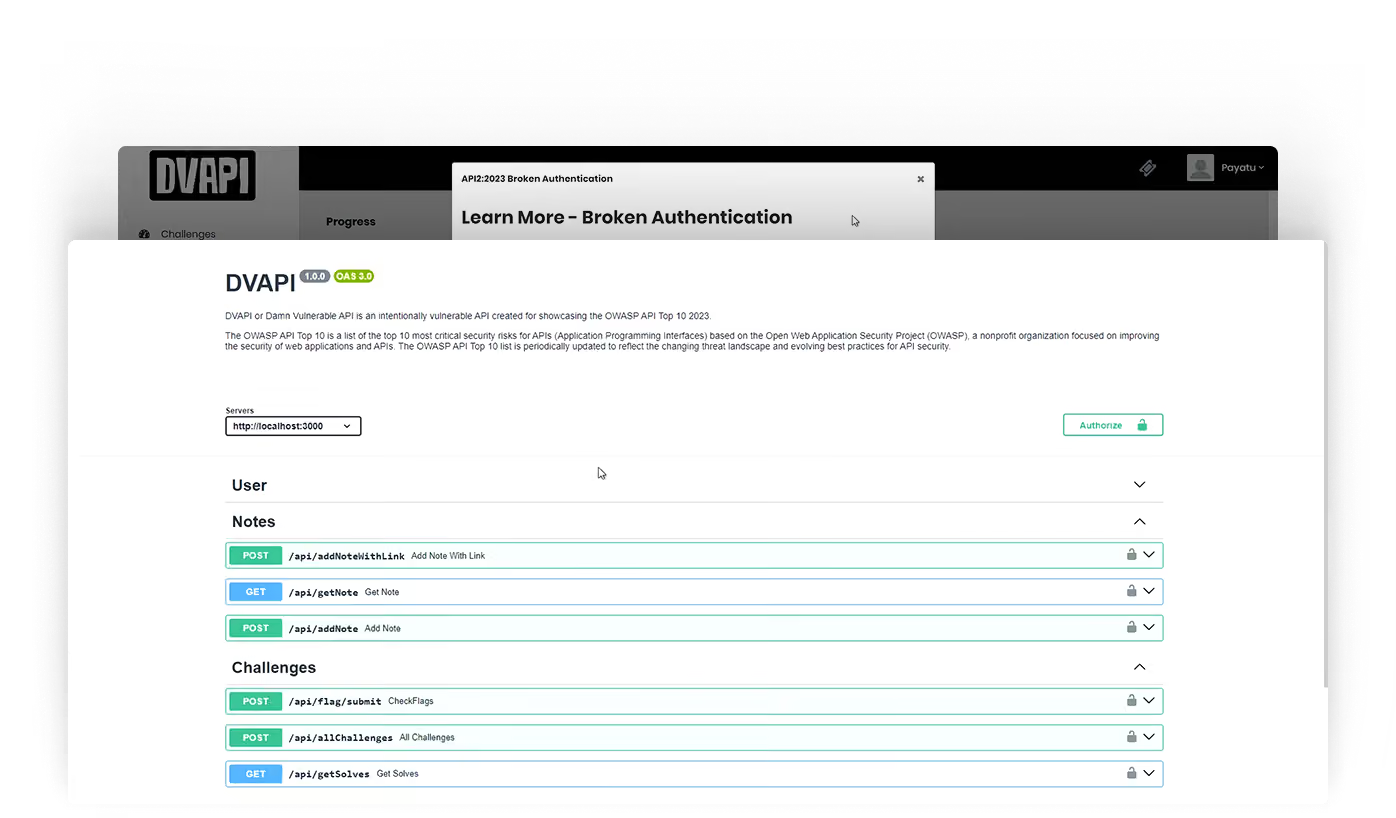
The road ahead
The vulnerability catalog
50+ modules span every major mobile vulnerability class, beginner to advanced. Here are three the full set ships in the app.
Auth
Broken Object Level Authorization
API 1
Auth
Broken Authentication
API 2
Auth
Broken Object Property Level Authorization
API 3
Auth
Unrestricted Resource Consumption
API 4
Auth
Broken Function Level Authorization
API 5
where it takes you
Ten flags later, you get it.
Reading the OWASP API Top 10 gives you the names. Exploiting all ten in DVAPI turns them into something you can spot in a real API. That is the point of the lab: the list becomes a skill.
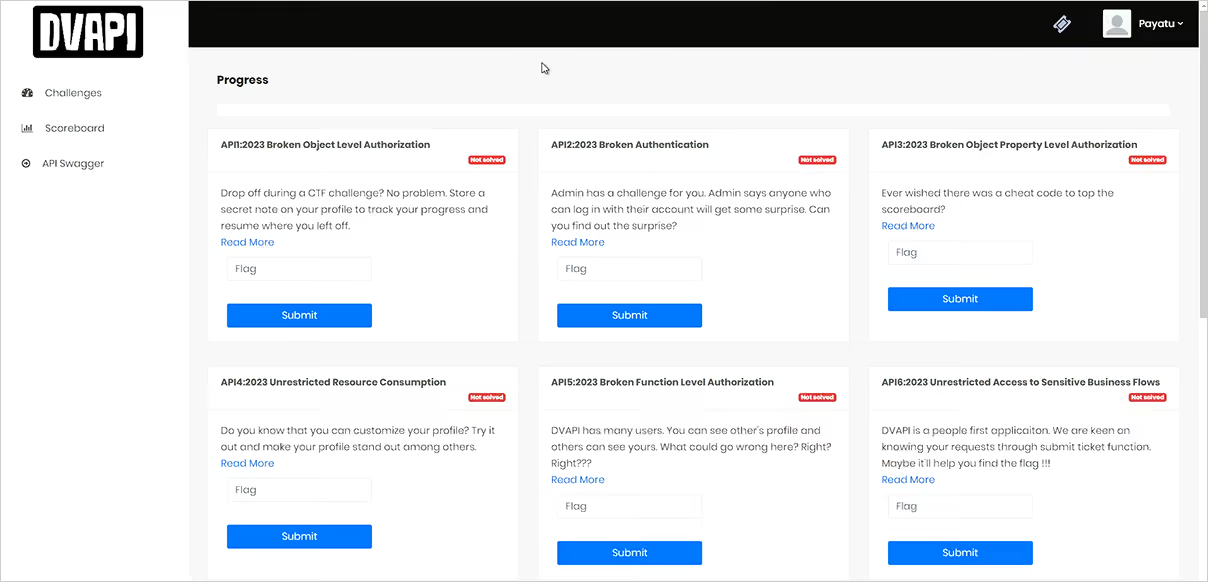
Get set up
Follow the steps below
DVAPI runs locally in Docker. Clone the repo, bring it up, open it in your browser, and you are on challenge one.
Docker
Recommend
Clone the repo.
git clone github.com/payatu/DVAPI
Spin it up.
docker compose up -build
Open the app at
127.0.0.1:3000
Point your tools. Hit it with
curl


Manual
Without Docker
Install dependencies from the repo README.
Run the API server and confirm it responds.
Open the flag-submission panel in your browser.
Start with API1 (BOLA) to confirm everything works.

DVAPI is intentionally vulnerable. Run it locally in an isolated environment, and never expose it to the public internet.
FAQ
Questions Web Application teams ask us.
What is Web Security Testing?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
What vulnerabilities are tested during a Web Security Assessment?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
How is Web Security Testing different from a vulnerability scan?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
When should we perform Web Security Testing?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
What do we receive after the Web Security Assessment?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
Can Web Security Testing identify business logic vulnerabilities?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.


