
The device, the app, the cloud.
We test the whole chain.
A connected device is never alone. It talks to a mobile app, a wireless link, and a cloud backend, and attackers hop from the weakest one to the rest. We test the whole ecosystem, from the chip to the cloud.




The question that matters
Your device is secure.
Your app is secure.
Your cloud is secure.
But has anyone tested what happens when an attacker moves between them?
Your app is secure.
Your cloud is secure.
But has anyone tested what happens when an attacker moves between them?
WHY MOST IoT Security TESTINGs FALL SHORT
Testing the device alone leaves the doors around it open
The device is only part of the story. The app that controls it, the wireless protocols, and the cloud it reports to are all ways in. Test one and skip the rest, and you've left the easy paths open.
Most IoT Security Vendors
Scan the network and calls it done
Use automated tools to find debug ports
Give up on chips that are hard to read
Run automated scans only
One tester for the whole device
Send a report and exits
Payatu
Opens the device up: full hardware teardown and PCB board analysis

Finds hidden debug ports manually, even when tools can't
Pulls firmware off any chip, however protected
AI-native and research-led: our own tools (EXPLIoT, BUS Auditor) plus deep manual analysis
A specialist for each part: hardware, firmware, and wireless protocol
Ranks findings by severity, then re-tests the fixes
What we test
Chip to cloud
We scope to what matters most in your device, then test every layer a real attacker would.
Circuit board & chips
Debug ports
Firmware
BLE
Zigbee
Wi-Fi
The Mobile app
Cloud & APIs
The Update Mechanism
Circuit board & chips
Debug ports
Firmware
BLE
Zigbee
Wi-Fi
The Mobile app
Cloud & APIs
The Update Mechanism
Hardware
Hardware Disassembly and PCB reversing
Finding hidden debug ports (UART, JTAG)
Pulling data straight off the chips
Verifying the tamper and cloning resistance
Hardware
Firmware
Extracting and reading the firmware
Identifying the Hardcoded sensitive info like password, keys or certificates
Insecure update mechanisms
Backdoors and hidden logic
Firmware
Connected ecosystem
The mobile app that controls it
Wireless links (BLE, Zigbee, Wi-Fi, LoRa)
The cloud backend and its APIs
Data leaking between device and cloud
Connected ecosystem
Hardware
Hardware Disassembly and PCB reversing
Finding hidden debug ports (UART, JTAG)
Pulling data straight off the chips
Verifying the tamper and cloning resistance
Firmware
Extracting and reading the firmware
Identifying the Hardcoded sensitive info like password, keys or certificates
Insecure update mechanisms
Backdoors and hidden logic
Connected ecosystem
The mobile app that controls it
Wireless links (BLE, Zigbee, Wi-Fi, LoRa)
Insecure update mechanisms
The cloud backend and its APIs
The cloud backend and its APIs
Data leaking between device and cloud
Process
How it works
Simple, step by step, from opening the device to confirming the fix.
Understand the device
You tell us what the device does and what matters most. We plan the test around it.
01
Open it up
We take the device apart, map the board, and find the ports and chips worth attacking.
02
Attack the whole system
We go after the wireless, the app, and the cloud, and see how far one weak link goes.
04
Get the firmware
We pull the firmware off the device and read it for passwords, keys, and flaws.
03
Explain what we found
Every issue in plain language, ranked by how much it would hurt the business.
05
Fix
We offer remediation support to fix each issue.
06
Process
How it works
Simple, step by step, from opening the device to confirming the fix.
Understand the device
You tell us what the device does and what matters most. We plan the test around it.
01
Open it up
We take the device apart, map the board, and find the ports and chips worth attacking.
02
Get the firmware
We pull the firmware off the device and read it for passwords, keys, and flaws.
03
Attack the whole system
We go after the wireless, the app, and the cloud, and see how far one weak link goes.
04
Explain what we found
Every issue in plain language, ranked by how much it would hurt the business.
05
Fix
We offer remediation support to fix each issue.
06
Real world impact
Real applications, real findings.


Testimonials
What IoT teams say about working with us

Payatu's focus on in-depth defence, quality, and proactive approach to all their services were precisely what our fast-growing publicly listed company needed.
Payatu's Services have helped us in ensuring that not only do we exceed strict compliance standards, but also ensure that security is not just a tick box exercise in our organisation. We have been able to make security an integral part of...
Payatu's Services have helped us in ensuring that not only do we exceed strict compliance standards, but also ensure that security is not just a tick box exercise in our organisation. We have been able to make security an integral part of...
Payatu delivered a 360-degree penetration testing exercise across our web applications and internal network. Their structured, methodical approach and deep technical understanding were evident throughout the engagement. They didn’t just give us a list of vulnerabilities, they provided actionable insights that helped to improve our security posture. The engagement was constructive.
WHY PAYATU
Why device makers pick us
We break devices at the chip and read the code that runs them. Few teams in the world go this deep.
OSCP, OSCE, GXPN & eWPTX, plus hardware certs
ISO 17025 accredited CERT-In empanelled
Founders of Nullcon &
hardwear.io
hardwear.io
CVEs in IoT platforms, embedded OS & wireless
Creators of EXPLIoT & BUS Auditor
Our own hardware lab



What you get
The whole story, not just a scan result.
Complete explaination
Exactly what we found and how we got there, in plain words your team can follow.
What it means for the business
Each issue ranked by real-world impact, not just a severity score.
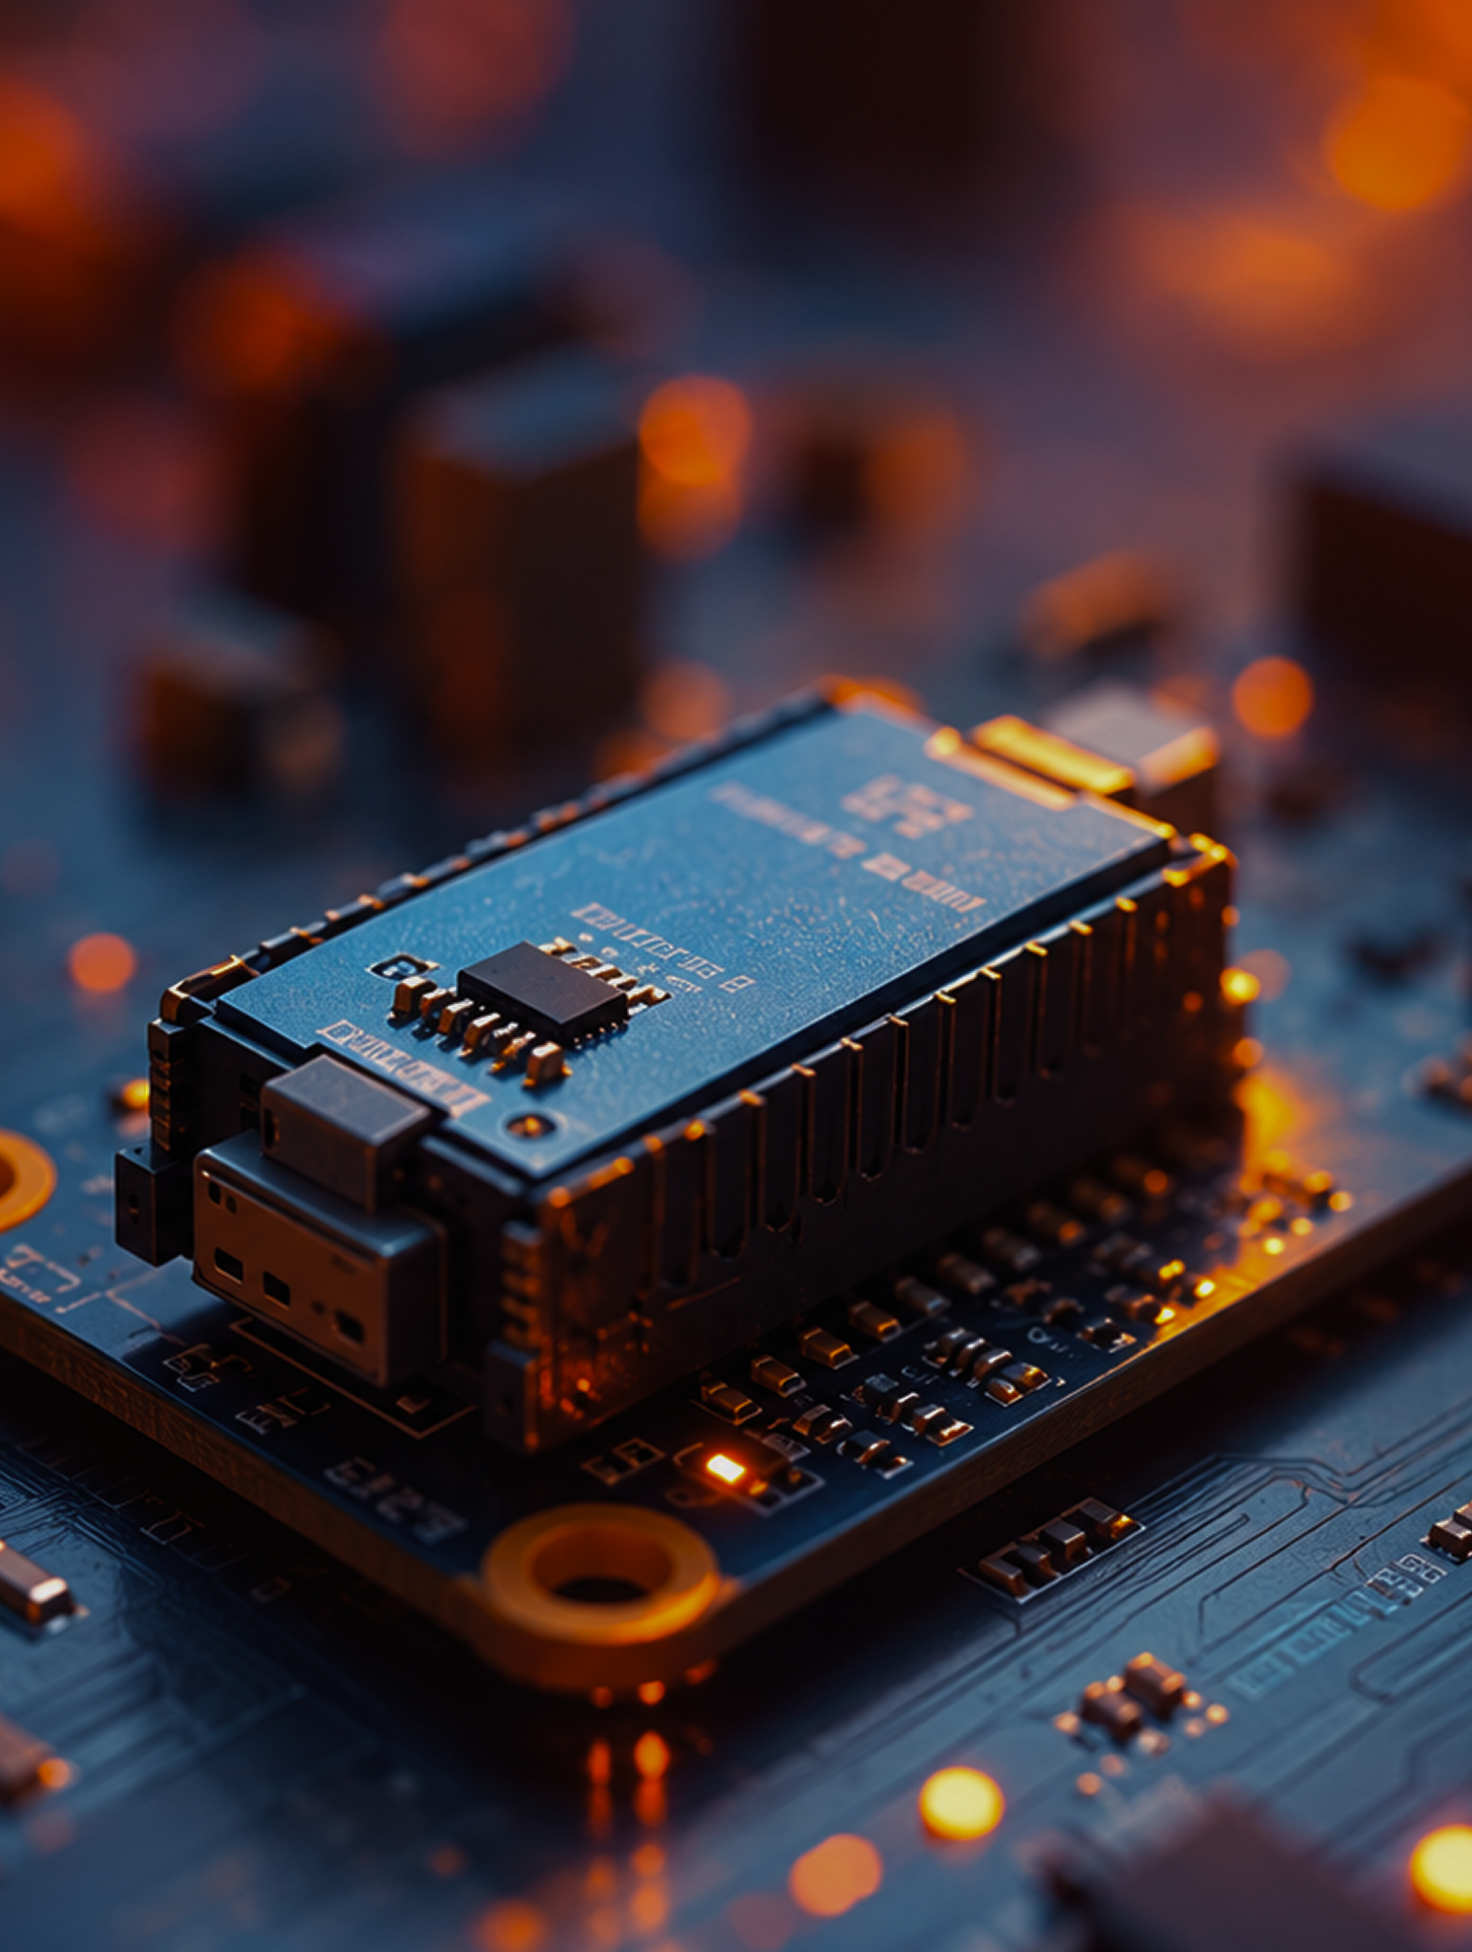
The proof
Photos, extracted firmware, and evidence behind every finding.
The fix, then a re-check
Clear fixes for your engineers, hardware and design advice, and a retest to confirm.


Want to get your IoT security assessed?
Talk to a security researcher and discuss the security posture of your company


Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.