Your certificate should mean your security actually works.

We're an accredited certification body, and a security firm that finds real vulnerabilities every day.

So, when we certify your ISO 27001 or Cyber Security Management System, the certificate reflects security that holds up, not just paperwork that's in order.
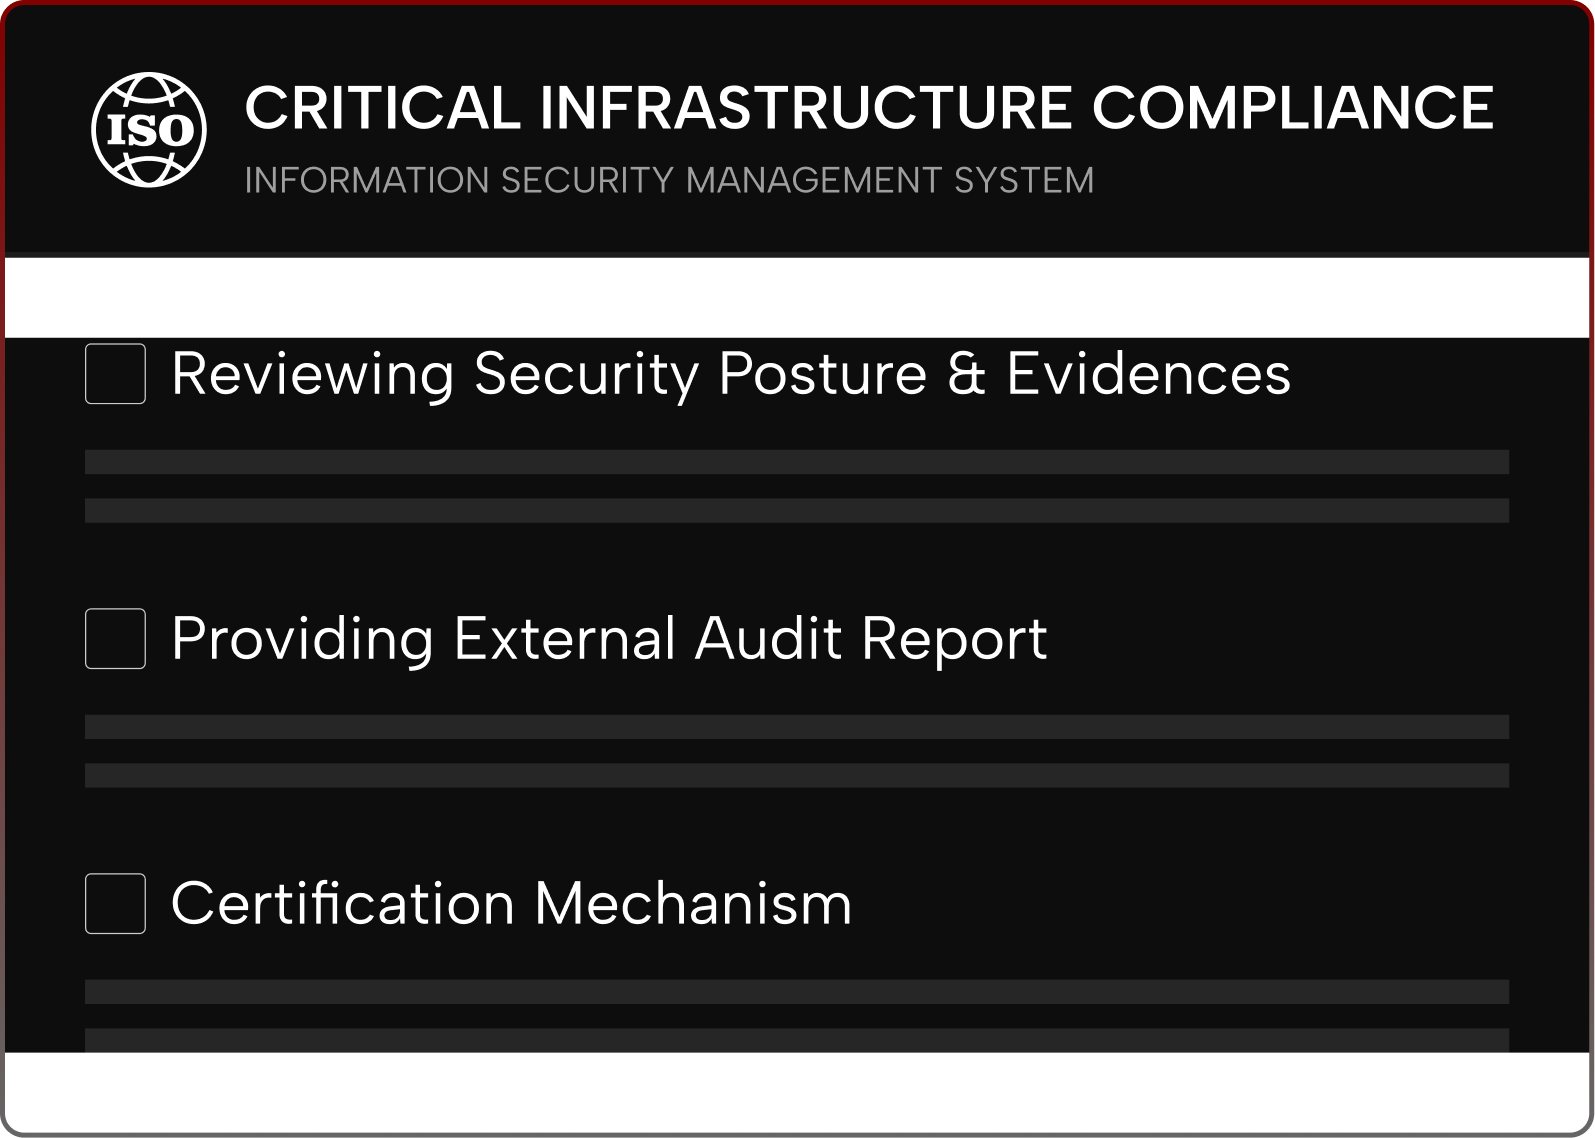
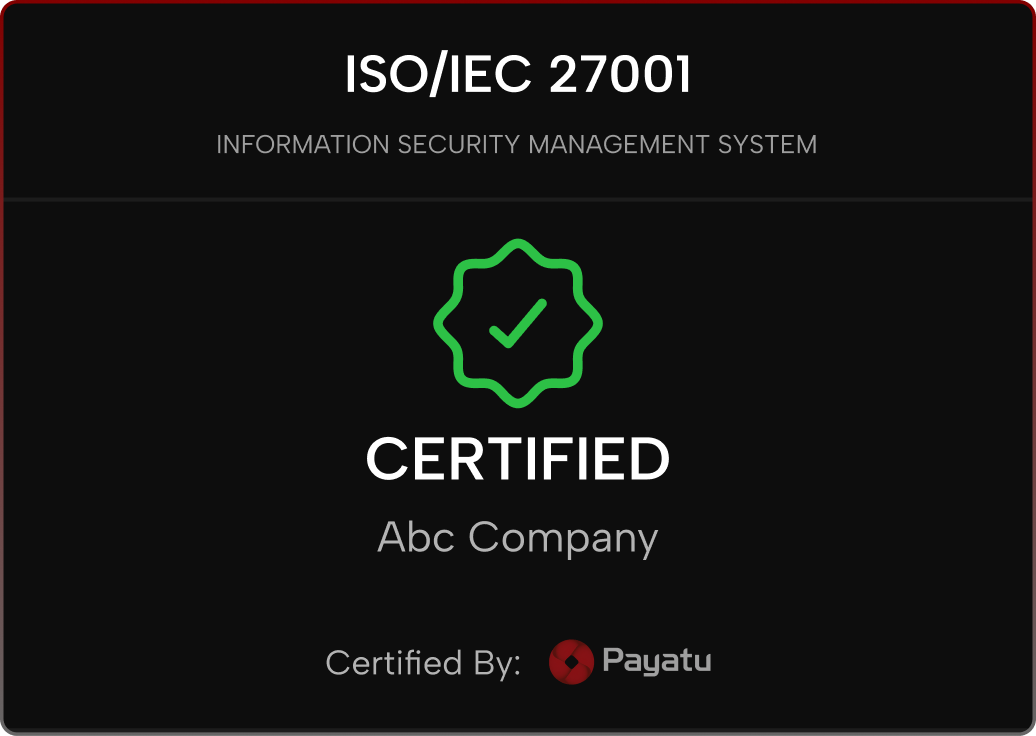
Checklist interface titled Critical Infrastructure Compliance with subheading Information Security Management System, featuring unchecked items: Reviewing Security Posture & Evidences, Providing External Audit Report, and Certification Mechanism.White checkmark inside a green square background symbolizing approval or confirmation.White checkmark inside a green square background symbolizing approval or confirmation.White checkmark inside a green square background symbolizing approval or confirmation.ISO/IEC 27001 Information Security Management System certification badge for Abc Company with a green checkmark icon and certification by Payatu.
Faint curved orange-red light streak on a dark black background with small scattered light dots.

The question that matters

Your customers ask for a certificate to trust you. But if it came from a body that only checks paperwork, what is it really worth?
WHY THE CERTIFIER MATTERS

A certificate is only as good as the body behind it

Anyone can hand out a logo for your website. A certificate that customers and regulators actually trust comes from an accredited, impartial body that checks whether your security truly works.

That's the difference between formality and real assurance.
Most Certifiers
Sells certificates as a formality
Auditors who've never seen a real attack
Checks that documents exist
Self-declared or unaccredited
A logo for your website
Certificate issued, then forgotten
Payatu
AI-native and research-led: certification backed by real security testing
Auditors who are also offensive security researchers
Checks that your controls actually work
NABCB-accredited, verifiable on IAF CertSearch
A certificate your customers and regulators trust
Yearly surveillance that keeps it valid and honest
What Certify

And how deep we look

We certify your management system against the standards your customers ask for, checking that the controls actually work.
ISO 27001:2022 (ISMS)
Cyber Security Management System (Level 1)
 Risk assessment
Statement of Applicability
Access control
Incident management
Business continuity
Supplier & vendor risk
ISO 27001:2022 (ISMS)
Cyber Security Management System (Level 1)
 Risk assessment
Statement of Applicability
Access control
Incident management
Business continuity
Supplier & vendor risk

Governance & policy

Information security policy
Roles & responsibilities
Statement of Applicability
Management commitment
Gradient background with smooth transition from dark blue on the lower left to deep red on the lower right, blending into black at the top.
Governance & policy

Controls & operations

Access control
Cryptography & data protection
Operations & monitoring
Incident management
Dark background with a bright orange and yellow glowing light streak on the right side, fading into blackness.
Controls & operations

Risk & resilience

Risk assessment & treatment
Supplier & third-party risk
Business continuity
Internal audit & improvement
Risk & resilience
Gradient background with smooth transition from dark blue on the lower left to deep red on the lower right, blending into black at the top.
Governance & policy
Information security policy
Roles & responsibilities
Statement of Applicability
Management commitment
Dark background with a bright orange and yellow glowing light streak on the right side, fading into blackness.
Controls & operations
Access control
Cryptography & data protection
Operations & monitoring
Incident management
Risk & resilience
Risk assessment & treatment
Supplier & third-party risk
Business continuity
Internal audit & improvement
Process

How certification works

A formal, accredited process, from application to renewal.

Apply

You share your scope and management system. We confirm the standard and plan the audit.
01

Stage 1 audit

We review your documents and readiness, and flag anything to fix before the main audit.
02

Certification decision

An independent committee reviews the findings, so no single auditor decides alone.
04

Stage 2 audit

An on-site audit of how your controls actually work, not just how they're written down.
03

Certificate granted

On success, your certificate is issued and listed publicly, verifiable on IAF CertSearch.
05

Surveillance & re-certification

Yearly surveillance keeps it valid, with re-certification at the end of the cycle.
06
Process

How certification works

A formal, accredited process, from application to renewal.

Apply

You share your scope and management system. We confirm the standard and plan the audit.
01

Stage 1 audit

We review your documents and readiness, and flag anything to fix before the main audit.
02

Stage 2 audit

An on-site audit of how your controls actually work, not just how they're written down.
03

Certification decision

An independent committee reviews the findings, so no single auditor decides alone.
04

Certificate granted

On success, your certificate is issued and listed publicly, verifiable on IAF CertSearch.
05

Surveillance & re-certification

Yearly surveillance keeps it valid, with re-certification at the end of the cycle.
06
Process
How certification works
A formal, accredited process, from application to renewal.

Apply

You share your scope and management system. We confirm the standard and plan the audit.
01

Stage 1 audit

We review your documents and readiness, and flag anything to fix before the main audit.
02

Stage 2 audit

An on-site audit of how your controls actually work, not just how they're written down.
03

Certification decision

An independent committee reviews the findings, so no single auditor decides alone.
04

Certificate granted

On success, your certificate is issued and listed publicly, verifiable on IAF CertSearch.
05

Surveillance & re-certification

Yearly surveillance keeps it valid, with re-certification at the end of the cycle.
06
Testimonials

What compliance teams say about working with us

Small white square with the top left corner cut out, creating a diagonal edge.
neoeyed logo in blue lowercase letters.
Video thumbnail showing a man named Carthic Kameshwaran, Head of Delivery at moEYED, speaking directly to the camera in a blue shirt.

Carthic Kameshwaran

Head of Delivery - neoEYED

Small white square with the top left corner cut out, creating a diagonal edge.
Stylized logo spelling the word 'nkash' with a geometric shape resembling an 'E' at the start in a gradient of blue shades.
Man in a light blue shirt speaking indoors with a potted plant and framed picture on a green wall behind him.

Arockiaraj Martin

CISO- Enkash

Small white square with the top left corner cut out, creating a diagonal edge.
Logo featuring a stylized purple circle with an inner dot next to the text 'Butn' in purple font on a black background.
Payatu's focus on in-depth defence, quality, and proactive approach to all their services were precisely what our fast-growing publicly listed company needed.
Payatu's Services have helped us in ensuring that not only do we exceed strict compliance standards, but also ensure that security is not just a tick box exercise in our organisation. We have been able to make security an integral part of...
Simran Gambhir

Chief Information Officer - Butn, Sydney

Small white square with the top left corner cut out, creating a diagonal edge.
CheckRed Security company logo with a stylized red cloud and checkmark icon next to the black and red text.
Payatu delivered a 360-degree penetration testing exercise across our web applications and internal network. Their structured, methodical approach and deep technical understanding were evident throughout the engagement. They didn’t just give us a list of vulnerabilities, they provided actionable insights that helped to improve our security posture. The engagement was constructive.

Sushil Vanve

Director of Engineering - CheckRed

WHY PAYATU

Why organizations certify with us

Most certificates prove you filled in the forms. Ours proves your security actually works, because the body behind it tests security for a living.
Certificates verifiable on IAF CertSearch
India's first ISO 17025 - accredited security lab
Certin logo with stylized text and a graphic element resembling a circuit or connection symbol.
CERT-In empanelled
Icon of a gray document with three horizontal lines and a red dot on the left side, all inside a white circular background.
NABCB-accredited certification body
Minimalist icon of a person sitting behind a rectangular desk with a red dot in the center.
Auditors who are also security researchers
Icon showing two gray angle brackets facing inward with a red dot in the center, representing a coding or programming symbol on a white circular background.
Bound by a published code of impartiality
Circle with a gradient of red shades, transitioning from dark red at the top to bright red at the bottom.Solid red symmetrical shape with pointed top and bottom edges, resembling an elongated lens or a leaf.
White text reading 'Stronger, trusted organizations' on a solid black background.
White outlined certificate icon with a red seal at the top center above the text 'Certification Expertise' on a black background.
White text 'Beyond Compliance Audits' below a white square target symbol with a red dot in the center on a black background.
What you get

A certificate that means something.

An accredited certificate

Recognised by the customers and regulators who ask for it, not a self-made logo.

A public, verifiable listing

Your ISO 27001:2022 certificate on IAF CertSearch, so anyone can confirm it.
A hand emerging from a glowing sleeve holds three semi-transparent folder icons illuminated with orange light on a dark background.

A detailed audit report

Exactly where you stand against the standard, confidential to you, with clear actions.

Ongoing assurance

Yearly surveillance and re-certification that keep your certificate valid and honest.
FAQ

Questions Web Application teams ask us

What is Web Security Testing?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
What vulnerabilities are tested during a Web Security Assessment?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
How is Web Security Testing different from a vulnerability scan?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
When should we perform Web Security Testing?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
What do we receive after the Web Security Assessment?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
Can Web Security Testing identify business logic vulnerabilities?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.