
Secure the Medtech. Protect the patient data.
Medical devices monitor vitals, deliver drugs, and keep people alive. If one can be hacked, patient safety is at risk.
We test every layer, hardware, firmware, and software, and produce evidence the regulating bodies now require.
We test every layer, hardware, firmware, and software, and produce evidence the regulating bodies now require.
Talk to a MedTech Security Expert


Trusted by Medtech Teams
A cyber risk is a clinical risk.
A device can be attacked through its wireless link, its app, or the hospital network. You can't always take it offline to fix it. Many run for years, and some are inside the patient. That raises the bar for security.
How we help
We test how far an attacker could move from your device into the wider network.

Attack-path testing from the device outward
Red teaming across devices and hospital systems
01
How we help
We test your device and backend to find from where the patient data (PHI) can be leaked.
Data-protection testing across device, app, and cloud
Findings aligned to HIPAA and GDPR
02
How we help
We show the real impact and how to contain it, so a single flaw can't take down entire healthcare.
Ranked by safety and continuity, not just CVSS
Detection and response tailored to hospital networks
03
A cyber risk is a clinical risk.
A device can be attacked through its wireless link, its app, or the hospital network. You can't always take it offline to fix it. Many run for years, and some are inside the patient. That raises the bar for security.
01 THE NETWORK
One weak device exposes them all.
Hospital networks run hundreds of connected devices (IoMT), many of them old and unpatched. Attackers look for the one that lets them in.
How we help
We test how far an attacker could move from your device into the wider network.

Attack-path testing from the device outward
Red teaming across devices and hospital systems
01
02 THE DATA
Health records outsell credit cards.
Health data is worth more to attackers than card numbers, and ransomware that halts healthcare gets paid.
How we help
We test your device and backend to find from where the patient data (PHI) can be leaked.
Data-protection testing across device, app, and cloud
Findings aligned to HIPAA and GDPR
02
03 THE IMPACT
A breach can stop a hospital.
The impact isn't limited to one device; it can be – halted hospital operations, wrong treatment, and compromised patient records
How we help
We show the real impact and how to contain it, so a single flaw can't take down entire healthcare.
Ranked by safety and continuity, not just CVSS
Detection and response tailored to hospital networks
03
The chain we test
Device and firmware
01
Wireless and gateway
02
Hospital network (IoMT, HL7, DICOM)
03
Cloud and device APIs
04
Patient records (EHR / PHI)
05
What We Deliver
One partner for the whole chain
From the device in a patient's hand to the records in the cloud, a Payatu service for each link.
Whole-device security testing
The complete device: firmware, hardware, wireless, and the software that runs it.

Medical device and IoMT security
Connected devices, from the silicon and firmware up to the wireless links.
Compliance
Compliant and Secure in Practice
We don't check boxes. We show what an attacker could do, then document it as evidence accepted by auditors.
Standard
What it requires
How Payatu helps
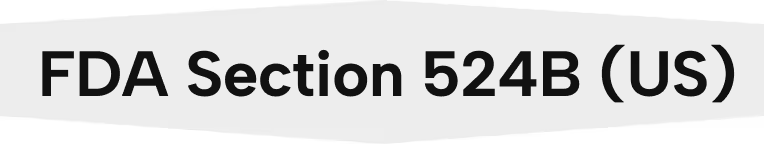
Cyber devices need a secure design, a plan to monitor and patch vulnerabilities, and a SBOM.
Threat modelling, testing, SBOM review, and submission-ready evidence.
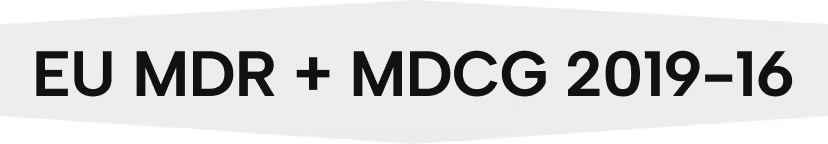
Software devices must be secure by design and kept up to date, with evidence.
Gap assessment against MDCG 2019-16, plus security testing.
The medical-software lifecycle standard, plus the security activities alongside it.
Secure development lifecycle review and testing.
Safety risk management, with a security risk assessment.
A security risk assessment that feeds your ISO 14971 file.
Protecting patient data: health information (HIPAA, US) and personal data (GDPR, EU).
We test how the device and backend store and move patient data.

WHY PAYATU
Top 1% researchers conducting your assessments
ISO/IEC 17025
India's first accredited cybersecurity testing lab. Findings that stand up to scrutiny.
CERT-In empanelled
Recognised by the government for security auditing. ISO 27001 and 9001 certified.

Researcher-led
Deep manual testing, backed by original security research.
Nullcon & hardwear.io
We founded two of the security conferences the industry learns from.
DSCI Excellence Award
Recognised as one of India's best cybersecurity services companies in Indian geography 2025.
FAQ
Questions Web Application teams ask us.
What is Web Security Testing?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
What vulnerabilities are tested during a Web Security Assessment?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
How is Web Security Testing different from a vulnerability scan?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
When should we perform Web Security Testing?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
What do we receive after the Web Security Assessment?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.
Can Web Security Testing identify business logic vulnerabilities?
Web Security Testing identifies vulnerabilities in web applications that attackers could exploit, helping organizations protect sensitive data and prevent security breaches.


Let's discuss your security maturity roadmap
Talk to a researcher who works in MedTech security every week - not a sales rep reading from a script.
