Cybersecurity Playbook for IPO-Bound Fintech Companies in India.
Investor diligence now reads your security programme the way it reads your books. This playbook maps the 24 months before listing into 6 phases, and names what has to be finished in each one.
GRC & Compliance
Fintech
Pages:
38
Format:
PDF
Level:
Executive
Updated:
Sep 2026
Key Takeaways
- The 4 regulators that put cyber on the board agenda: the SEC's 4-business-day incident disclosure rule, RBI's cybersecurity framework, SEBI's CSCRF, and CERT-In empanelled assessments.
- A 6-phase timeline from 24 months pre-IPO to post-listing, with the deliverable that closes each window.
- The 5 questions investors ask in diligence: board expertise, risk quantification in financial terms, incident response inside the disclosure window, third-party risk, and compliance history.
- A worked 2-year investment summary you can take into a board meeting, using FAIR to state cyber risk in rupees rather than in findings.
What's inside
Going public changes what a security programme is for. It stops being an IT function and becomes a disclosure item, read by underwriters, regulators and investors who are pricing your risk. The gap most fintechs hit is timing: the controls that satisfy diligence take 18 months to build and 3 weeks to fail an audit.
This playbook sets out the sequence. Each phase names what to build, who owns it, and what evidence a diligence team will ask to see. It is written for the CFO, CISO and board sponsor running the listing together, not for a security team working alone.
What the 38 pages cover
01
Executive summary for board and leadership
p. 3
What the board has to approve, and the disclosure rules that now apply across jurisdictions.
02
Strategic context: why cybersecurity matters in fintech IPOs
p. 4
The 4 risk factors specific to fintech, and what stakeholders evaluate at filing.
03
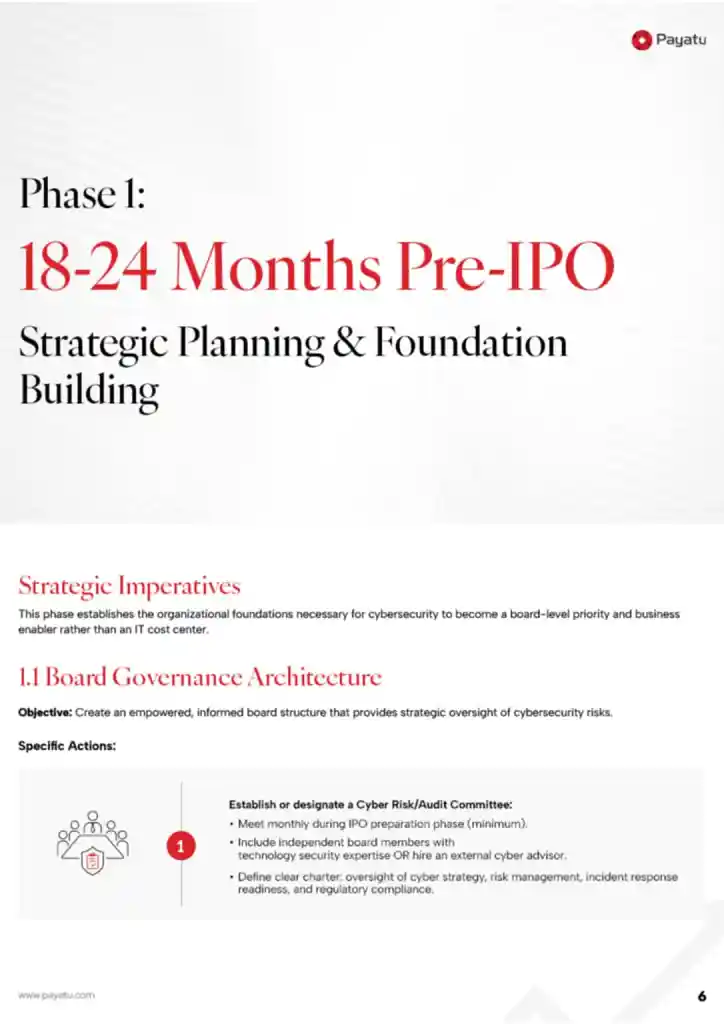
Phase 1 and 2: 12 to 24 months pre-IPO
p. 6
Strategic planning, governance foundation, and security framework implementation.
04
Phase 3 and 4: 3 to 12 months pre-IPO
p. 15
Risk disclosure preparation, compliance, and due diligence readiness testing.
05
Phase 5 and 6: filing to listing, and after
p. 30
Final validation, investor confidence, and continuous monitoring post-listing.
06
Financial summary: the 2-year investment
p. 34
What the programme costs, and how to argue its return in front of the board.
Look inside
A sample spread — the level of detail in every chapter.
Written by Payatu's GRC Team
Take the timeline into your next board meeting
The full 38-page PDF, with all 6 phases, the diligence checklist, and the investment summary laid out for board review.