Mastering React Native Application Pentesting.
A React Native app is a JavaScript bundle wearing a native shell. A standard Android checklist covers the shell and misses the bundle, which is where the logic, the endpoints and the secrets tend to sit.
Mobile Security
Cross-platform
Pages:
95
Format:
PDF
Level:
Intermediate
Updated:
Oct 2026
Key Takeaways
- How to tell a React Native build from a native one, and what the bridge means for where the application logic actually lives.
- Reverse engineering the JavaScript bundle, including Hermes bytecode, then editing, patching and repackaging the application.
- SSL certificate pinning bypass for React Native, which does not respond to the usual Android techniques.
- Identifying manually installed npm packages inside a shipped app, and a walkthrough of known React Native npm package CVEs.
What's inside
React Native began as a hackathon project and now ships in a large share of cross-platform apps. Pentesting one with a standard Android checklist covers the shell and misses the bundle, and the bundle is where the business logic, the endpoints and the hardcoded secrets tend to sit.
This guide covers the Android side in depth, and most of the techniques carry across to iOS React Native builds. It assumes basic Android pentesting knowledge and some JavaScript, then goes straight to the framework-specific attack surface: the bridge, the bundle, Hermes, pinning and the npm dependency chain.
What the 95 pages cover
01
What React Native is, and the bridge concept
p. 4
How JavaScript reaches native code, and why that boundary is the interesting part.
02
Reverse engineering React Native apps
p. 13
Getting from an APK back to readable bundle code.
03
Identifying a React Native build
p. 18
The indicators that tell you which methodology to run before you start.
04
Attack surfaces and static analysis
p. 25
The out-of-the-box test cases specific to React Native, beyond the usual Android set.
05
Editing, patching and modifying Hermes bytecode
p. 41
Changing behaviour in the bundle, including when Hermes is in the way.
06
SSL certificate pinning bypass
p. 71
Why the standard techniques fail here, and what works instead.
07
npm packages: identification and CVE walkthrough
p. 76
Finding what was installed manually, then working through the known package CVEs.
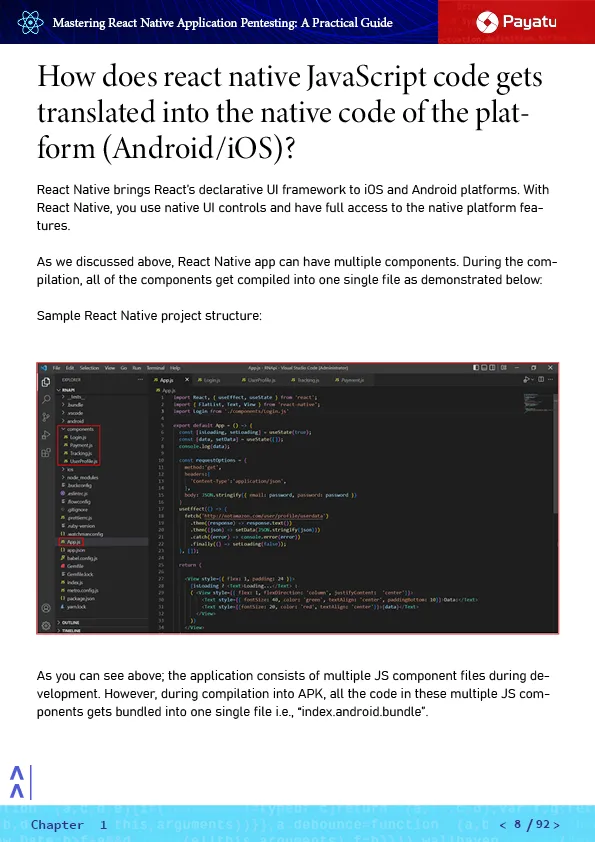
Look inside
A sample spread — the level of detail in every chapter.
Written by Payatu's mobile security team
Take the methodology into your next mobile assessment
The full 95-page PDF, with the bridge, the bundle, Hermes, pinning and the npm CVE walkthrough set out as a repeatable methodology.