Hands-On Internet of Things Hacking: The Masterclass.
Practical guide that starts at what an IoT attack surface is and end at fault injection on a live board. This is the Payatu IoT masterclass, written to be worked through with hardware in front of you.
IoT & Hardware
Masterclass
Pages:
233
Format:
PDF
Level:
Beginner to Advanced
Updated:
Oct 2026
Key Takeaways
- The full IoT attack surface broken down: storage, hardware interfaces (UART, JTAG, SWD, I2C, SPI), sensors, radio, network, mobile, cloud and web.
- Protocol chapters with attacks and mitigations for each: MQTT and broker hardening on Mosquitto and AWS IoT Core, CoAP, Bluetooth Low Energy and ZigBee.
- Hardware work you can repeat: PCB recon, chip identification, FCC ID lookups, debug port discovery with Bus Auditor and the DIVA board, and firmware extraction over SPI and I2C.
- Side-channel analysis and fault injection explained against real CVEs, plus 11 well-known IoT attacks from Mirai and Ripple20 to Sweyntooth and Amnesia:33.
What's inside
IoT security fails at the seams: a debug port left enabled, a firmware image sitting unencrypted on a flash chip, a ZigBee link key shipped as the default. Finding those means working at the hardware, not reading about it.
This masterclass runs from architecture and attack surface through protocols, radio, firmware and hardware, to side-channel and fault injection. Each part is written as a lab: the tools, the recon, the attack, and the mitigations. The hardware chapters use the EXPLIoT DIVA board and Bus Auditor, so every step is reproducible on a desk.
What the 233 pages cover
01
IoT introduction, architecture and attack surface
p. 22
High-level, functional and layered views, then the device, mobile, cloud, web and communication surfaces.
02
IoT top ten vulnerabilities
p. 40
The OWASP 2014 list alongside Payatu's own 2018 top ten, from hardcoded secrets to insecure cloud interfaces.
03
Protocols: MQTT, CoAP, BLE and ZigBee
p. 49
How each works, how each is attacked, and how to harden the broker or the stack.
04
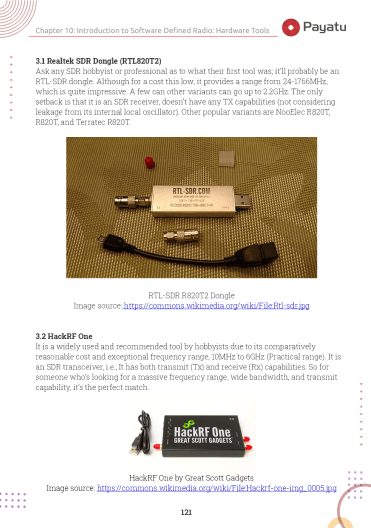
Software defined radio: hardware and software tools
p. 119
RTL-SDR, HackRF One, BladeRF and USRP, then recon, demodulation, decoding and attack.
05
Firmware reverse engineering
p. 134
Bare metal and full OS firmware, with Binwalk, QEMU, gdb-multiarch and Firmware Mod Kit.
06
Hardware: recon, debug ports, SPI, I2C, UART, JTAG and SWD
p. 140
Board analysis, chip identification, and extracting data from each interface in turn.
07
Side-channel, fault injection and famous IoT attacks
p. 212
Power, EM, timing and cache attacks, glitching techniques, and 11 real-world cases.
Look inside
A sample spread — the level of detail in every chapter.
Written by Payatu's IoT security research team
Work through it with the board in front of you
The full 233-page PDF, covering hardware, protocols, radio and firmware, written as a lab you can repeat with the EXPLIoT DIVA board and Bus Auditor.