Decoding NCIIPC's Conformity Assessment Framework.
CAF is not another checklist standard. It is a national assurance system built on 5 schemes, and it decides who is allowed to certify, inspect, consult and train across India's critical infrastructure. This whitepaper explains what changes, and what changes for you.
OT/ICS
India Regulation
Pages:
22
Format:
PDF
Level:
Intermediate
Updated:
Sep 2026
Key Takeaways
- What CAF actually is: NCIIPC's framework, developed with the Quality Council of India, covering people, processes, technology and governance across Critical Sector Entities.
- The 5 schemes in one place: Cybersecurity Management System certification, the inspection scheme for IT and ICS, CyberPros personnel certification, accreditation for consultancy organisations, and accreditation for training bodies.
- Whether CAF is mandatory, and what it maps to: ISO 27000, IEC 62443, NIST and CIS, set against the IT Act 2000, NCIIPC directives and CEA guidelines.
- Preparation split by who you are: a Critical Sector Entity, a consultancy organisation, a training body, or an individual practitioner.
What's inside
India's critical sectors already carry several overlapping cybersecurity mandates. CAF does something different. Rather than adding controls, it builds the assurance layer underneath them: who certifies a management system, who inspects an ICS, who is competent to consult, and who is accredited to train.
This whitepaper reads the framework scheme by scheme and says plainly what each covers and who it binds. The last section splits preparation by role, because a distribution licensee and a consultancy organisation are looking at completely different parts of the same framework.
What the 22 pages cover
01
Zoom out first: what is changing
p. 4
Why NCIIPC and QCI built an assurance framework rather than another control set.
02
So what exactly is CAF
p. 5
The core objectives, and the standards and Indian law it is built on.
03
The CAF ecosystem: 5 schemes, one purpose
p. 7
CSMS certification, IT and ICS inspection, CyberPros, consultancy and training body accreditation.
04
Is CAF mandatory, and what makes it different
p. 15
Where it binds, where it signals, and how it differs from a certification you already hold.
05
Preparing for CAF, based on who you are
p. 17
Separate preparation paths for CSEs, consultancies, training bodies and practitioners.
06
How Payatu can help
p. 20
Gap assessment, readiness support, and OT security work aligned to the framework.
07
About the author
p. 21
The SCADA security consultant who wrote it.
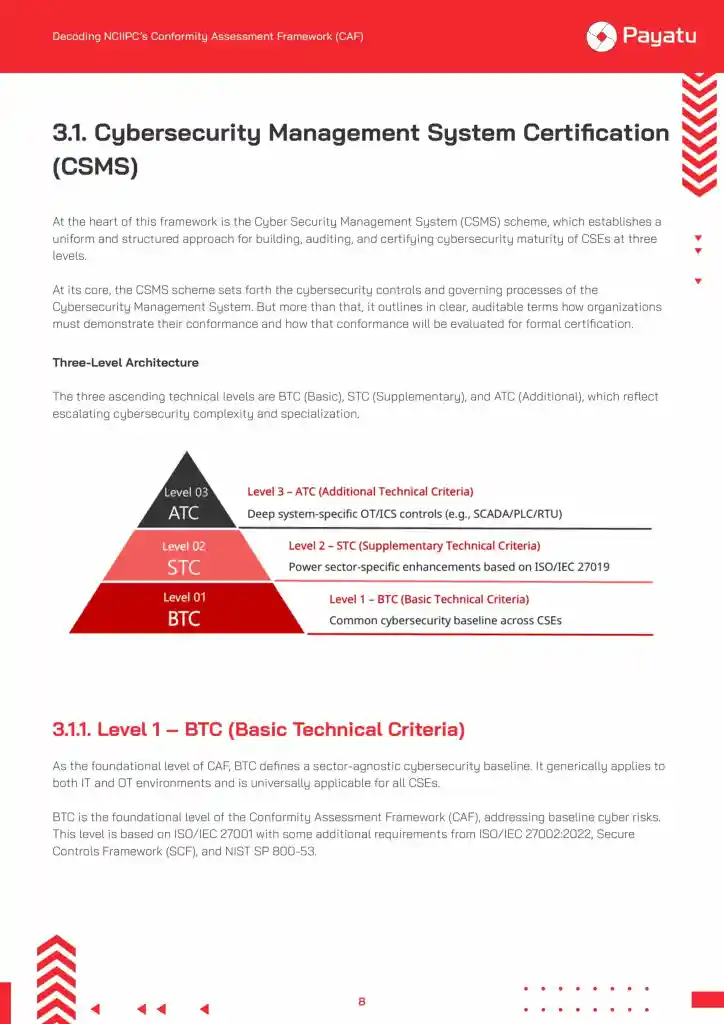
Look inside
A sample spread — the level of detail in every chapter.
Written by Payatu's OT security practice
Keep the decode on your desk
The full 22-page PDF, written to be printed, annotated and passed around. Scheme explanations on one side, the preparation path for your role on the other.