
Hacksys Extreme Vulnerable Driver



Key Takeaways
- HEVD is an intentionally vulnerable Windows driver for practising kernel exploitation.
- It covers bugs from stack and pool overflows to use-after-free and type confusion.
- Integer overflow, arbitrary overwrite and null pointer dereference bugs are also included.
- The driver was tested on Windows XP SP3, Server 2003 SP3 and Windows 7 SP1 (x86).
- Bundled exploits target Windows 7 SP1 x86 and need tweaks for other versions.
- The driver is built with the Windows Driver Kit and installed using OSR Driver Loader.
INTRODUCTION
HackSys Extreme Vulnerable Driver is intentionally vulnerable Windows driver developed for security enthusiasts to learn and polish their exploitation skills at Kernel level.
HackSys Extreme Vulnerable Driver caters wide range of vulnerabilities ranging from simple Buffer Overflows to complex Use After Frees and Pool Overflows. This allows the researchers to explore the exploitation techniques for all the implemented vulnerabilities.
WHY HACKSYS EXTREME VULNERABLE DRIVER?
I was giving a series of talks on Windows Kernel Exploitation at null Security Community’s Pune Chapter. So, I thought, it’s better to write a driver which has all the major vulnerabilities implemented in it. The idea to write the driver was to provide the attendees a better view of what’s happening behind the vulnerable code and also this will be of great help during my workshops and trainings.
VULNERABILITIES IMPLEMENTED
- Pool Overflow
- Use After Free
- Type Confusion
- Stack Overflow
- Integer Overflow
- Stack Overflow GS
- Arbitrary Overwrite
- Null Pointer Dereference
SCREENSHOTS
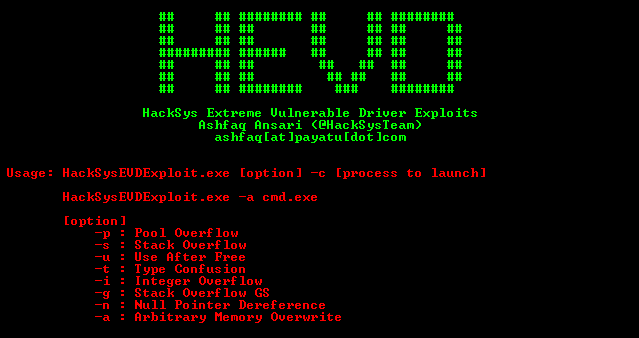
1) Help
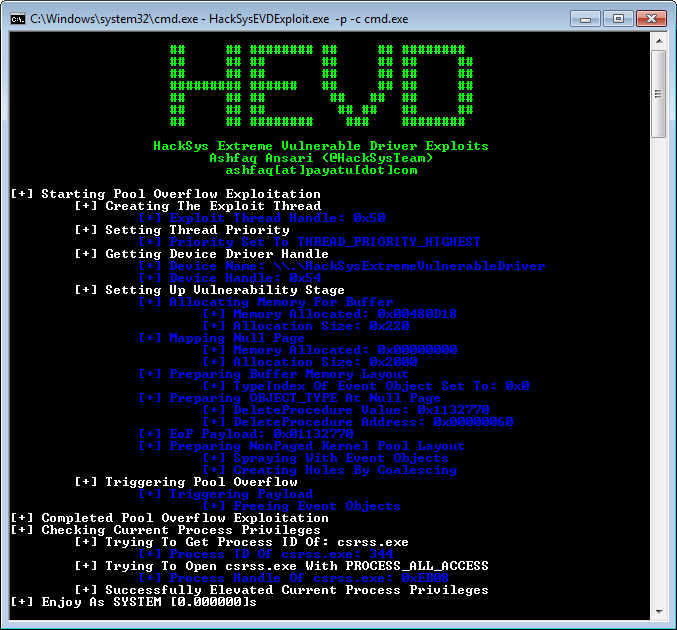
2) Exploit
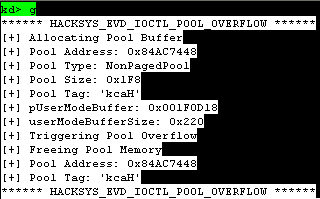
3) Driver Debug Print
4) SOURCE CODE
5) SUPPORTED WINDOWS VERSIONS :
This driver has been successfully tested on Windows XP SP3 (x86), Windows 2003 SP3 (x86) andWindows 7 SP1 (x86), but it can support Windows 8⁄8.1 (x86) too. Windows 8⁄8.1 support has not been tested now.
6) WHAT ABOUT EXPLOITS? : The exploits have been provided with this project. The exploit has been tested on Windows 7 SP1 (x86) and will need tweaking to support other versions of Windows OS.
7) BUILDING DRIVER + Install Windows Driver Kit
- Change %localSymbolServerPath% in bat and Build_HEVD_Vulnerable.bat driver builder
- Run the appropriate driver builder Build_HEVD_Secure.bat or Build_HEVD_Vulnerable.bat
INSTALLING DRIVER
Use OSR Driver Loader to install HackSys Extreme Vulnerable Driver
TODO
Yes, there are few more vulnerabilities I want to implemented in it like Use Of Uninitialized Variable Vulnerability and Time-Of-Check-To-Time-Of-Use (TOCTOU) Vulnerability. Another important vulnerability I want to implement is Memory Disclosure Vulnerability, this will help me to break KASLR on Windows 8 variant.
If you have ideas to propose, do contact me or raise a feature request/bug report via Github Issue Tracking page https://github.com/hacksysteam/HackSysExtremeVulnerableDriver/issues
SESSIONS CONDUCTED
- Windows Kernel Exploitation 1
- Windows Kernel Exploitation 2
- Windows Kernel Exploitation 3
- Windows Kernel Exploitation 4
- Windows Kernel Exploitation 5
WORKSHOPS CONDUCTED
BUG REPORT
Please file any bug report via GitHub Issue Tracker at the below given address:https://github.com/hacksysteam/HackSysExtremeVulnerableDriver/issue

Keep Reading





We break browsers before someone else does
This is the default text value

