PAYATU

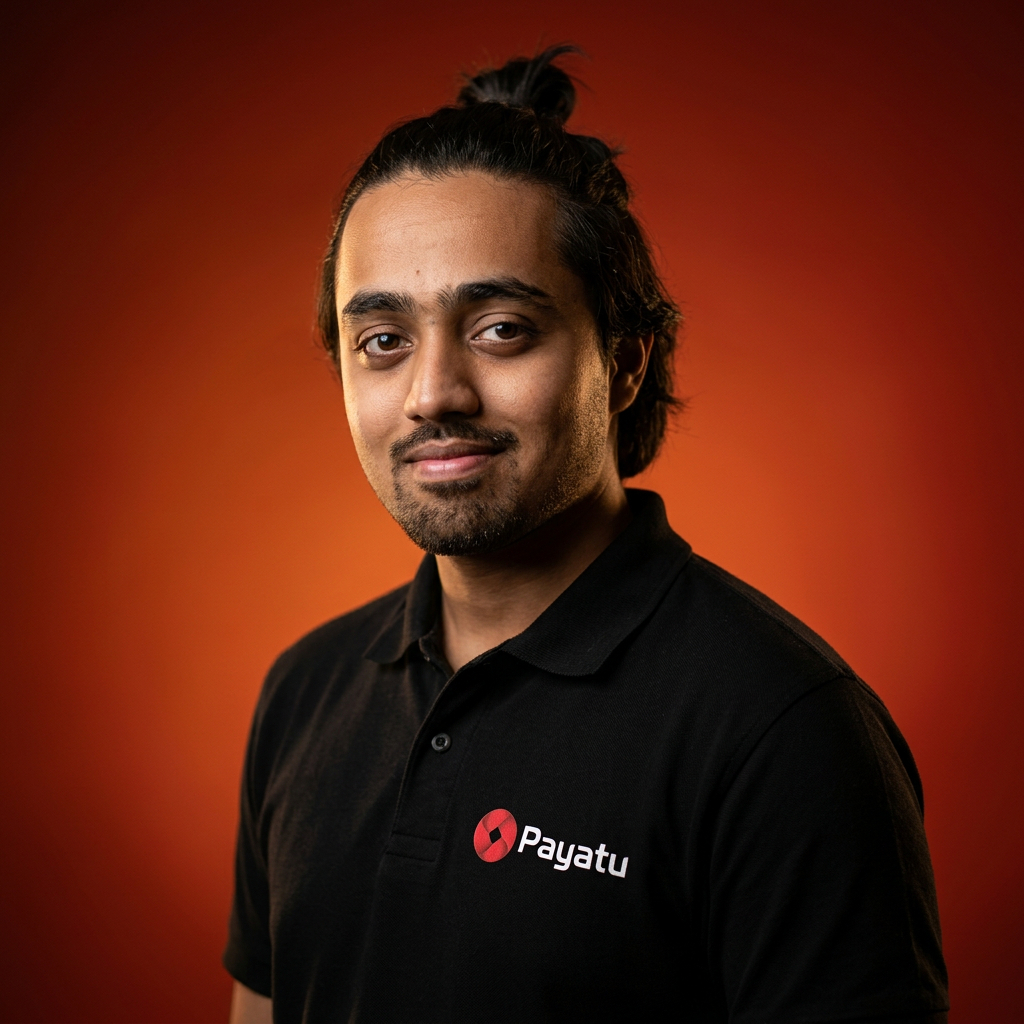
Dhabaleshwar Das

Security Consultant
Security Consultant at Payatu covering web, mobile and firmware security. Formerly Senior Security Consultant at Deloitte and a security researcher with NCIIPC, where he was ranked among India's Top 15 researchers (Q3 2023) for 200+ government-site vulnerabilities; discovered CVE-2026-7179 in Binwalk.
PAYATU

Dhabaleshwar Das

Security Consultant

CVEs published

Vulnerabilities discovered and responsibly disclosed. Each links to the Payatu advisory.
SAML 2.0 Authentication Bypass in SolarWinds Web Help Desk

Successful exploitation allows a remote unauthenticated attacker to bypass SAML authentication and impersonate an existing privileged user.
Enterprise & Mobile
Authentication & Access Bypass
Critical
Dark gray arrow pointing to the right on a transparent background.Dark gray arrow pointing to the right on a transparent background.

Path Traversal in Binwalk WinCE Extraction Leading to Arbitrary File Write and Code Execution

This vulnerability allows an attacker to craft a malicious firmware image that writes files outside the intended extraction directory when processed by a vulnerable Binwalk installation.
Developer Tools & Libraries
Remote Code Execution

Medium
Dark gray arrow pointing to the right on a transparent background.Dark gray arrow pointing to the right on a transparent background.

Insecure Deserialization Leading to Arbitrary Code Execution in datrie.Trie

This vulnerability allows a remote attacker to execute arbitrary code on the target system by tricking a victim into loading a malicious .trie file.
Developer Tools & Libraries
Remote Code Execution
Medium
Dark gray arrow pointing to the right on a transparent background.Dark gray arrow pointing to the right on a transparent background.

Talks & appearances

Conferences, podcasts and workshops.
No items found.

Articles by  

Dhabaleshwar Das

IoT & hardware
Exploit dev & reverse engineering
Binwalk Path Traversal Vulnerability: Turning Firmware Analysis into Code Execution
June 10, 2026
8 min
IoT & hardware
Exploit dev & reverse engineering
Security leaders
Researchers
For Security Leaders
Research & disclosures

The Bandits

Conferences, podcasts and workshops.
All
Bandits
Management

Aman Aryan

Consulting, Research and IT Head
Dark gray arrow pointing to the right on a transparent background.Dark gray arrow pointing to the right on a transparent background.

Aman Aryan

Consulting, Research and IT Head
Dark gray arrow pointing to the right on a transparent background.White arrow pointing diagonally upward to the right on a black square background.
Bandits
All

Abizer Naseem

Security Consultant
Dark gray arrow pointing to the right on a transparent background.Dark gray arrow pointing to the right on a transparent background.

Abizer Naseem

Security Consultant
Dark gray arrow pointing to the right on a transparent background.White arrow pointing diagonally upward to the right on a black square background.
All
Bandits

Ajay S.K

IoT Firmware Security Researcher
Dark gray arrow pointing to the right on a transparent background.Dark gray arrow pointing to the right on a transparent background.

Ajay S.K

IoT Firmware Security Researcher
Dark gray arrow pointing to the right on a transparent background.White arrow pointing diagonally upward to the right on a black square background.